
Blog
News, opinion and deep dives from the front line of security operations.
 Threat Research
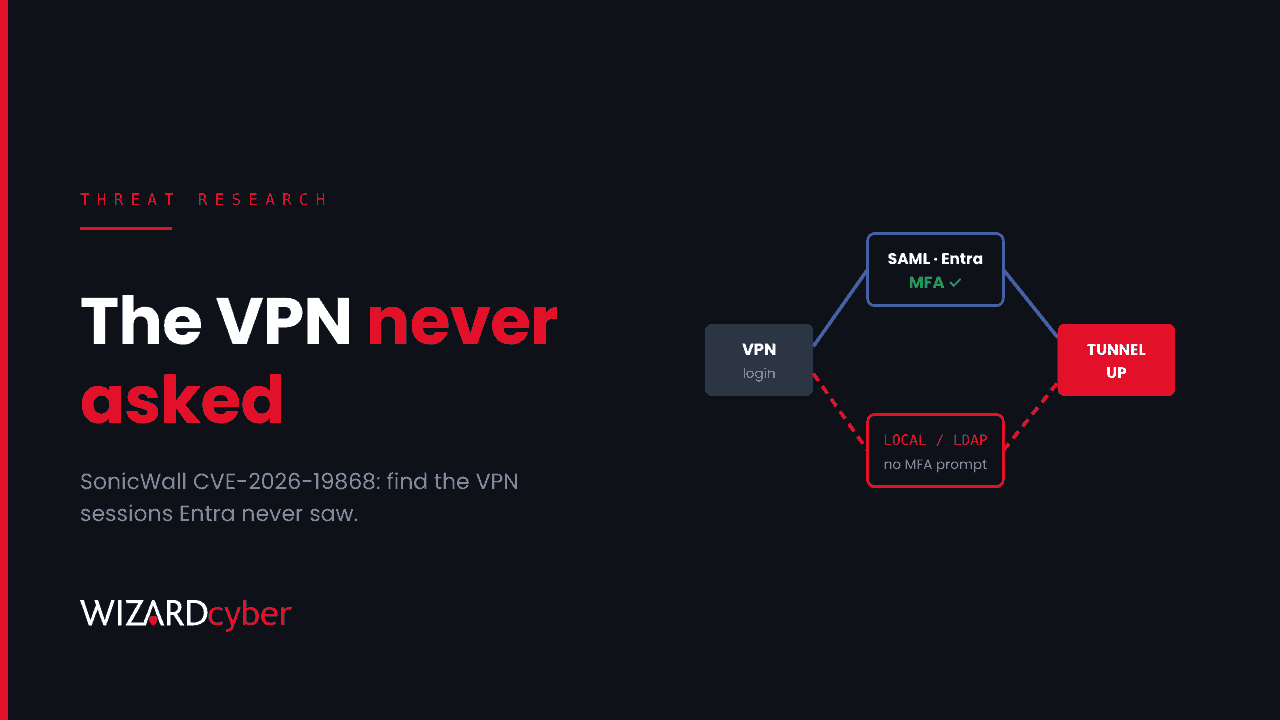
MFA Said Yes, The VPN Never Asked: Hunting Downstream Of The SonicWall SAML Bypass (CVE-2026-19868) In Entra And Active Directory
SonicWall's SSL VPN flaw let valid alternate credentials skip SAML and MFA. Find VPN sessions Entra never saw, then trace them into AD.
 Governance
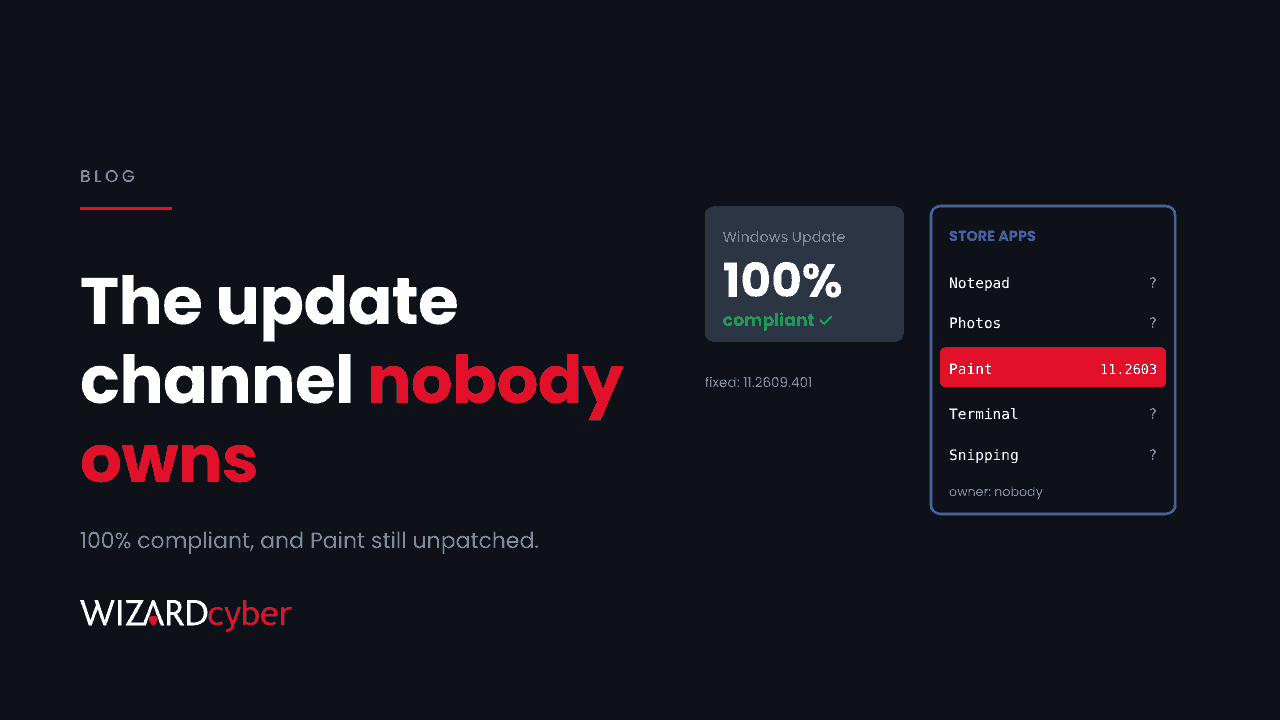
Paint Is Patched By The Store, Not Windows Update. Does Your Patch Report Know That?
A Paint RCE fix ships through the Microsoft Store, not Windows Update. Why Store and self-updating apps need an owner and a version check.
 Governance
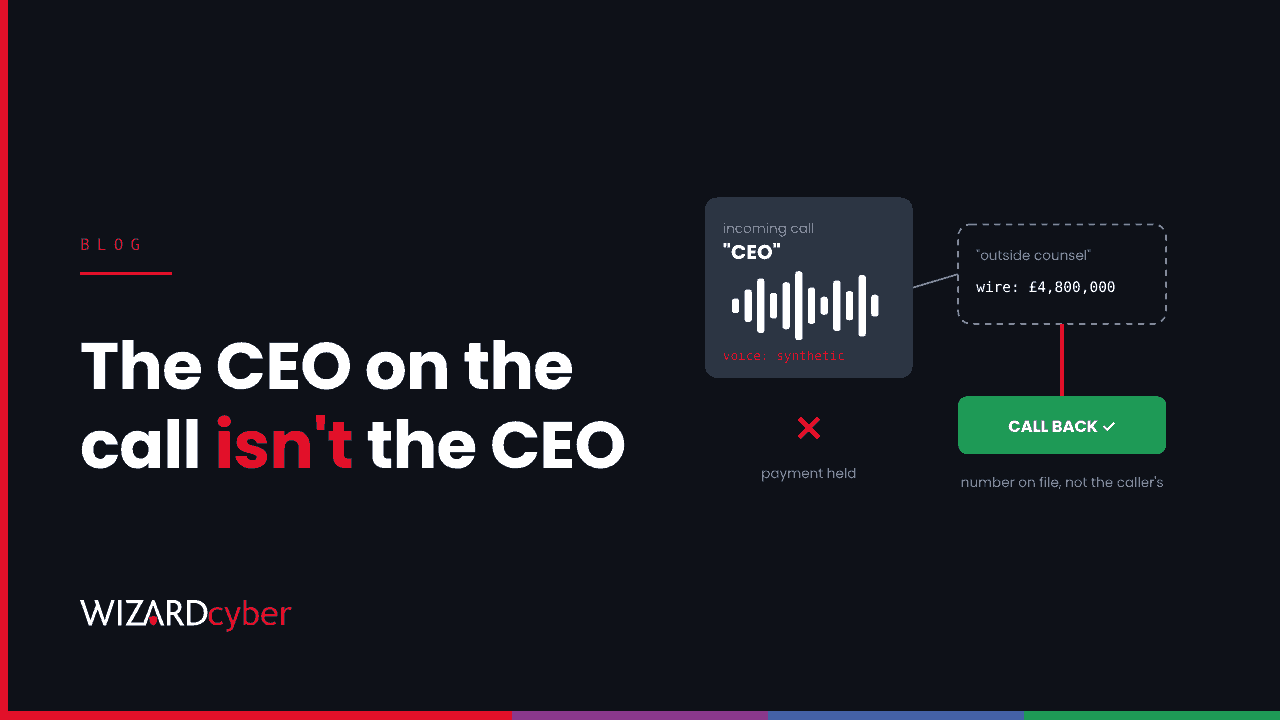
The CEO On The Call Isn't The CEO: $129 Million Says Payment Approvals Need A Second Channel
Cloned executive voices and fake lawyers took $129m from firms worldwide. Why payment approvals must verify the request, not the voice.
 Threat Research
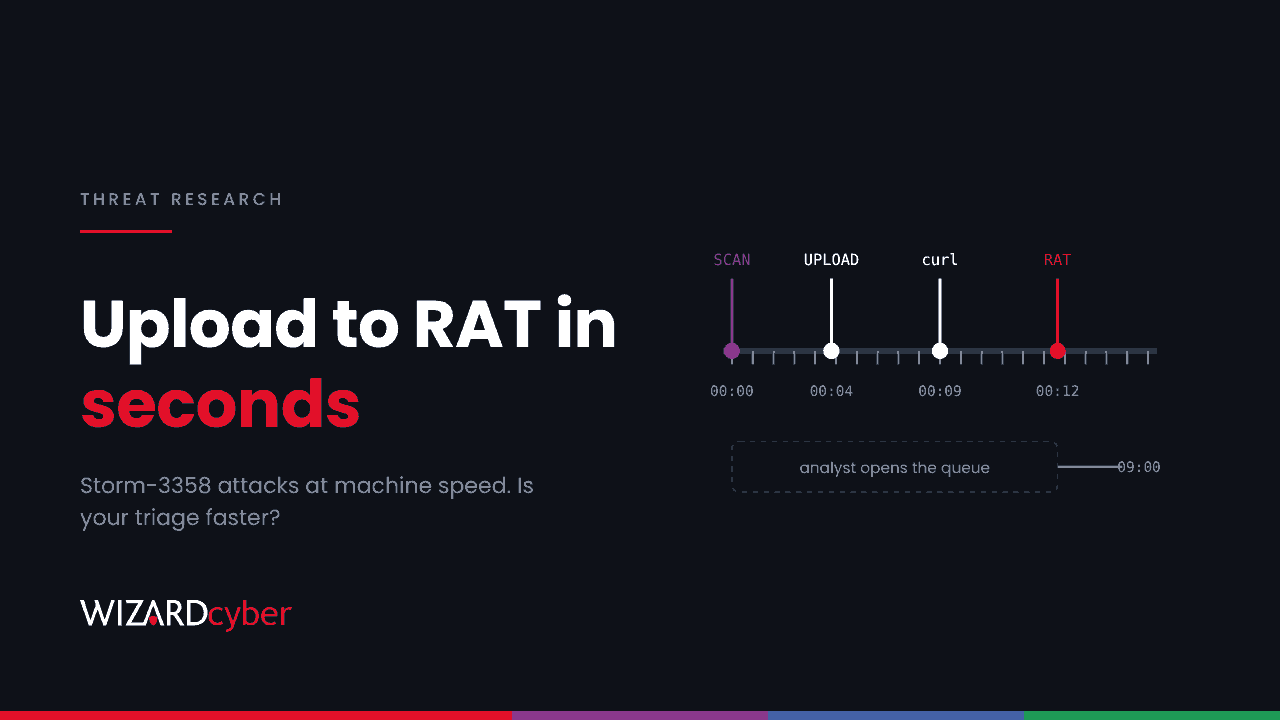
An Upload Field, Then A RAT In Seconds: Hunting Storm-3358's Machine-Speed Intrusions Against Financial Services
Storm-3358 uses AI agents to exploit upload and SSRF flaws, then pulls RATs with curl. Hunts for Sentinel and Defender, plus Microsoft's IOCs.
 Governance
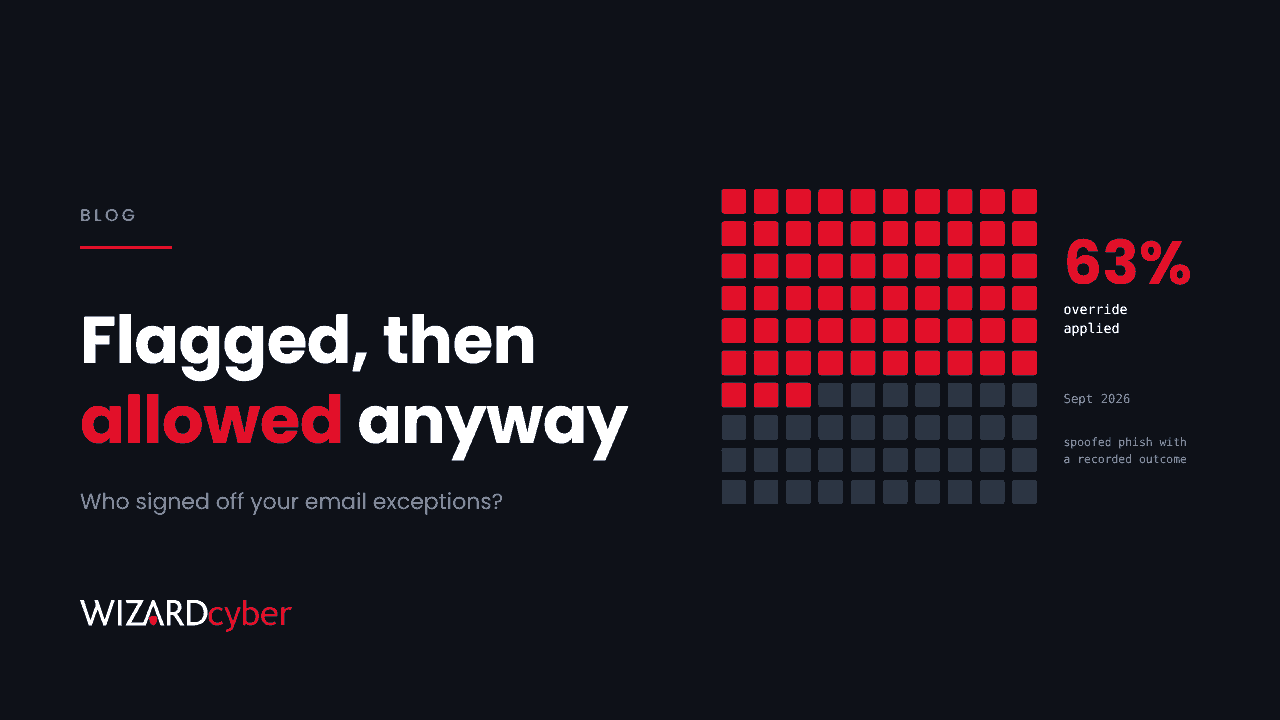
63% Of The Spoofed Phish Had An Exception Applied. Who Signed Off Your Allow-List?
Microsoft found overrides applied to 63% of spoofed malicious email with a recorded outcome. Why exceptions need owners, scope and an expiry date.
 AI Driven Security Operations
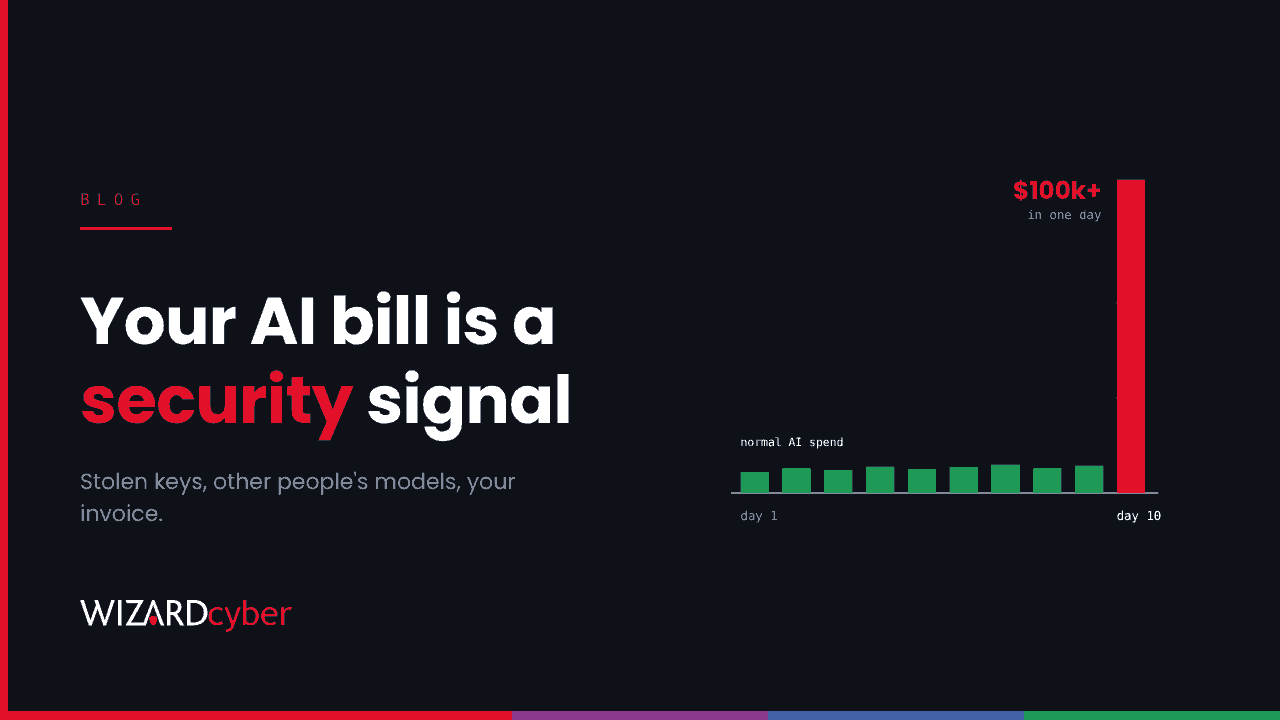
$100,000 A Day In AI Nobody Ordered: Your Cloud Bill Is Now A Security Signal
Attackers are running AI models on stolen cloud access, at up to $100,000 a day. Why AI spend belongs in the SOC, and what to watch in Azure.
 Threat Research
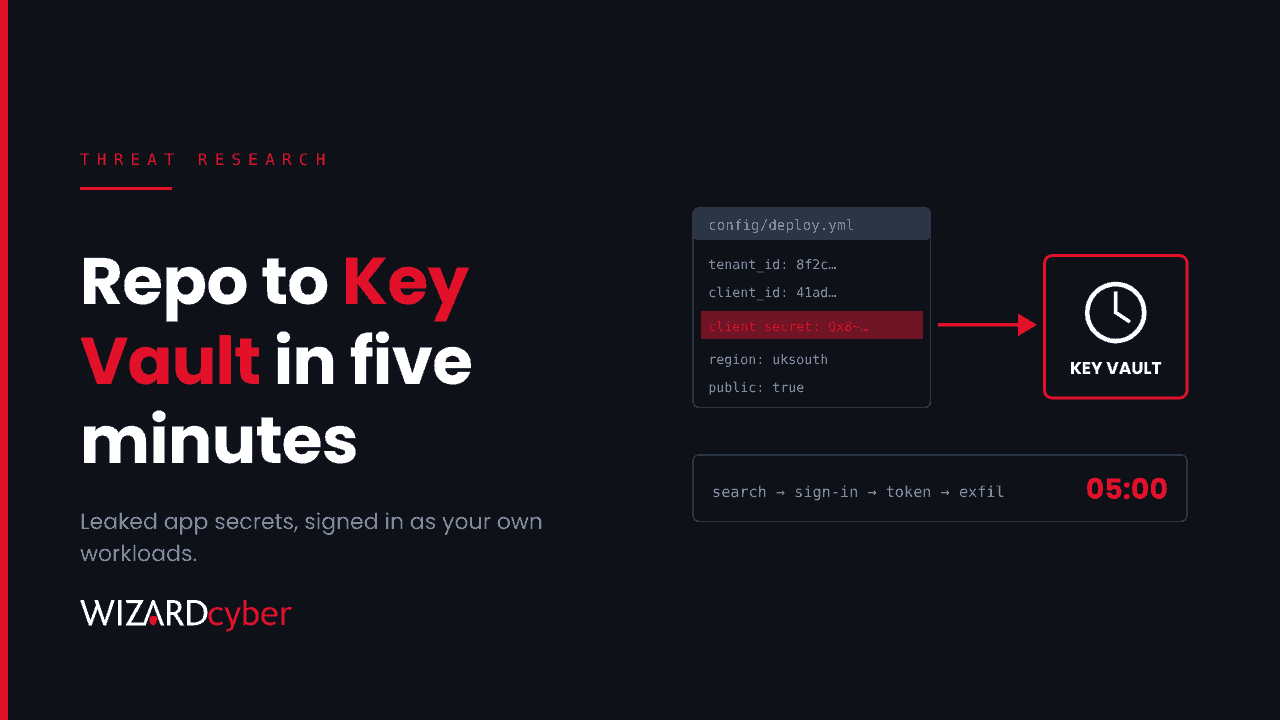
From A Public Repo To Key Vault In Five Minutes: Hunting The Agentic Secret-Harvesting Campaign In Entra ID And Azure
An AI-driven operator used leaked app secrets to sign in as victims' own workloads and raid Key Vault. What happened, and Defender and Sentinel hunts.
 Threat Research
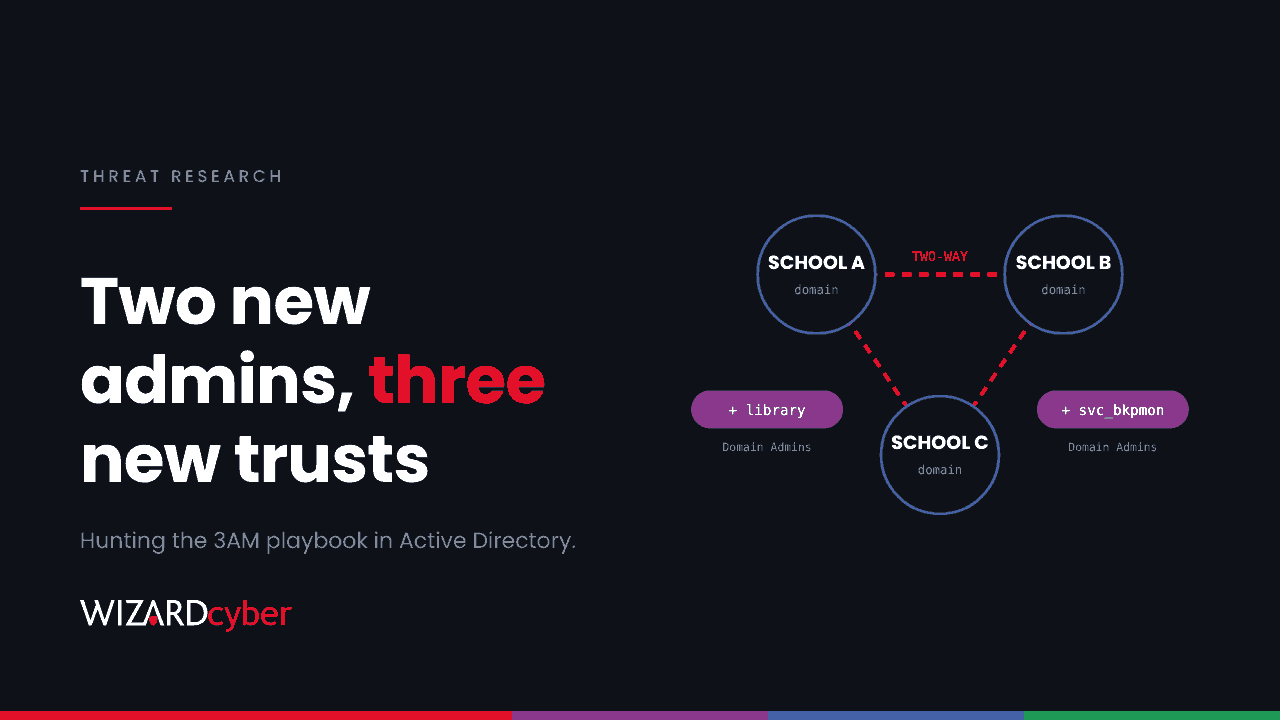
Two New Domain Admins And Three New Trusts: Hunting The 3AM Ransomware Playbook In Active Directory
3AM ransomware hit a UK school estate after nine nights of backup credential theft, new domain admins and new trusts. How to hunt each step in Defender.
 Governance
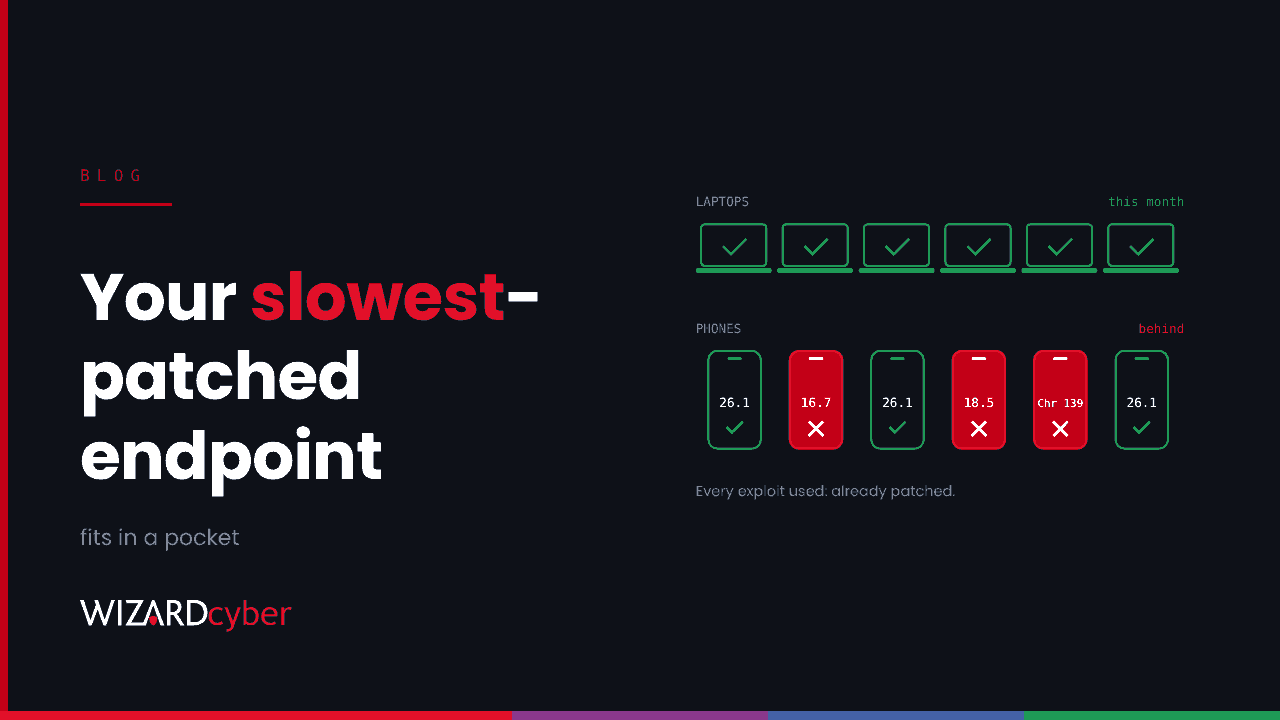
Every Exploit In The Chain Was Already Patched: Why Phones Are Your Slowest-Patched Endpoints
A nation-state crew stole phone data using only patched flaws. Who owns mobile patching, and how Intune minimum OS rules close the gap.
 Threat Research
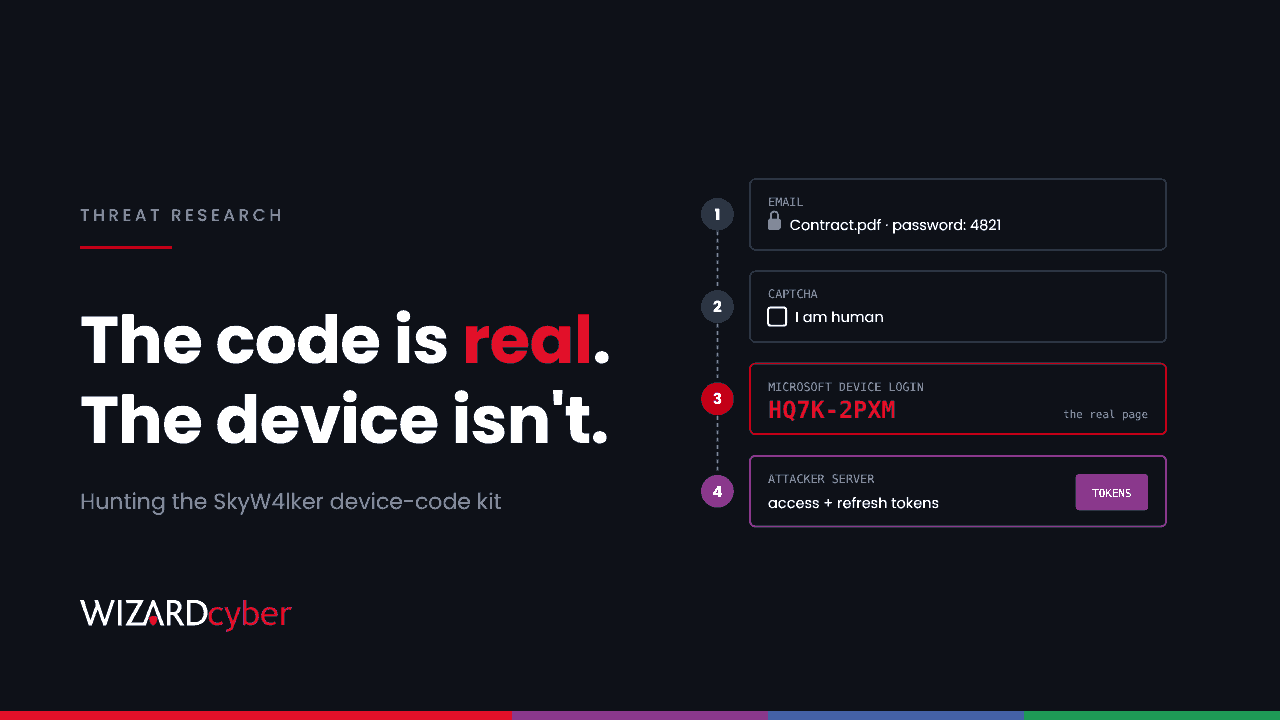
Password In The Email, Code On Microsoft's Page: Hunting The SkyW4lker Device-Code Kit In Microsoft 365
SkyW4lker gets users to enter an attacker's code on Microsoft's real login page. How the kit works, Defender and Sentinel hunts, and how to block it.
 Governance
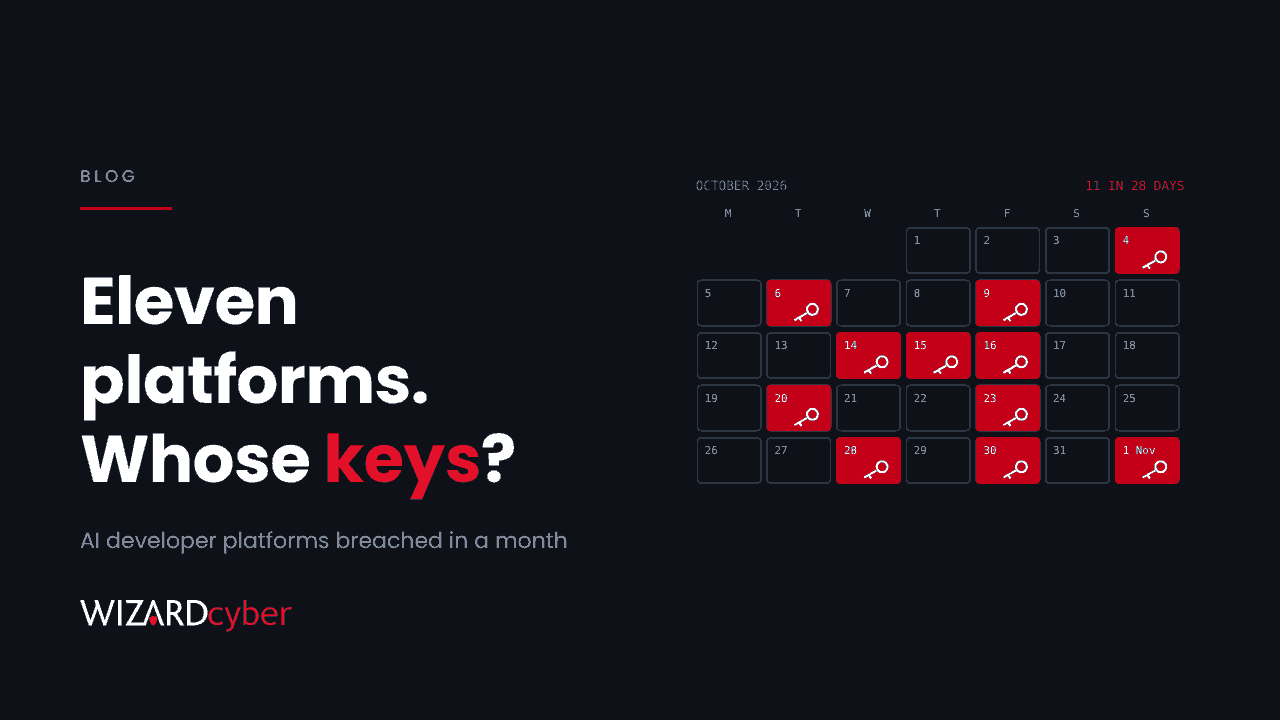
Eleven AI Developer Platforms Breached In 28 Days. Which Of Them Hold Your Tokens?
Attackers breached AI and developer platforms to steal customers' keys. Why these platforms are suppliers, and a register, reduce, rotate, watch routine.
 Threat Research
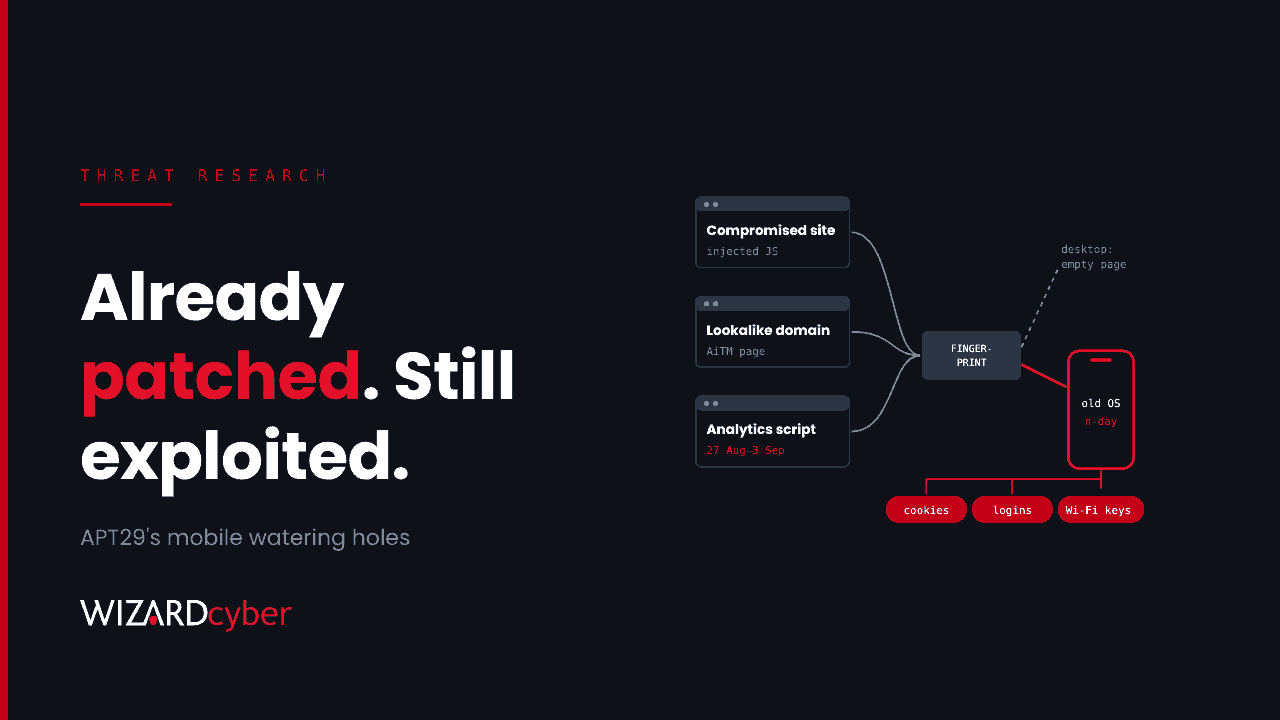
Patched Exploits, Poisoned Sites: Hunting APT29's Mobile Watering Holes From Defender And Intune
APT29 used poisoned websites and already-patched exploits to steal cookies from phones. How it worked, hunting queries, and the Intune fixes.
 Threat Research
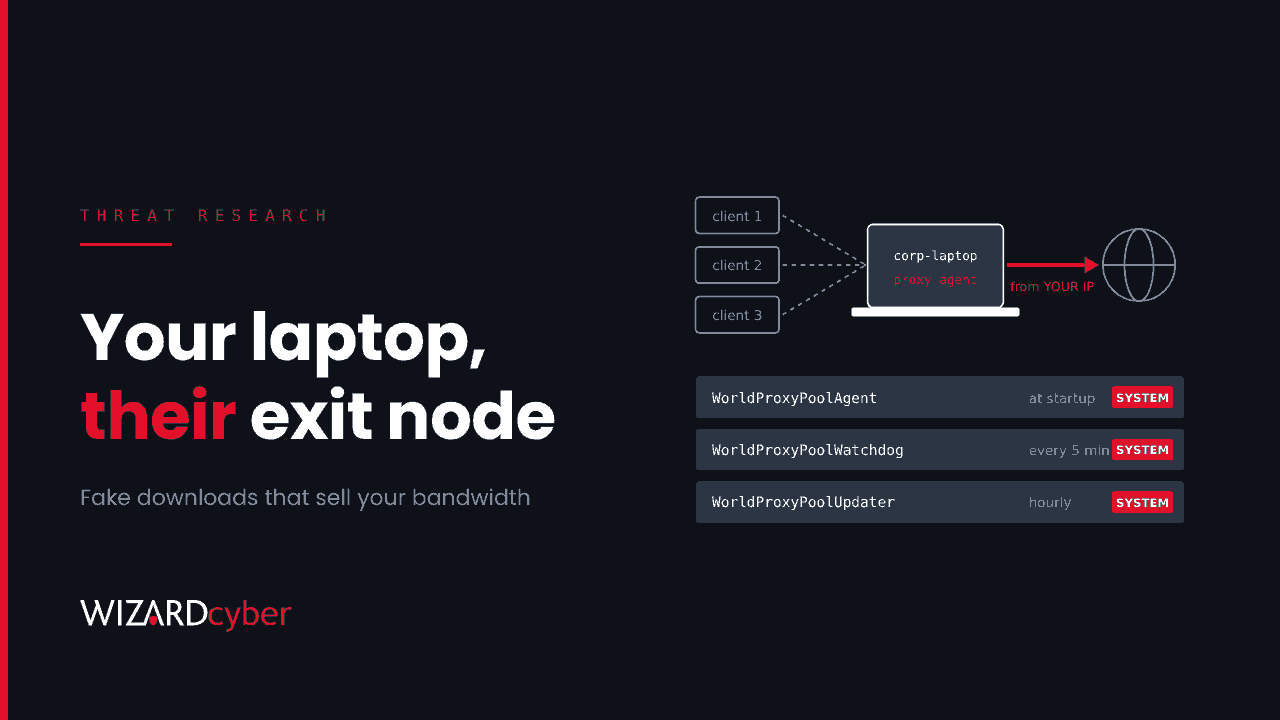
Your Laptop, Someone Else's Exit Node: Hunting Trojanised Inno Setup Installers And Proxyware In Defender
Fake downloads install proxyware and compute agents with SYSTEM scheduled tasks. How the chain works, and Defender hunts for every stage.
 Managed SOC
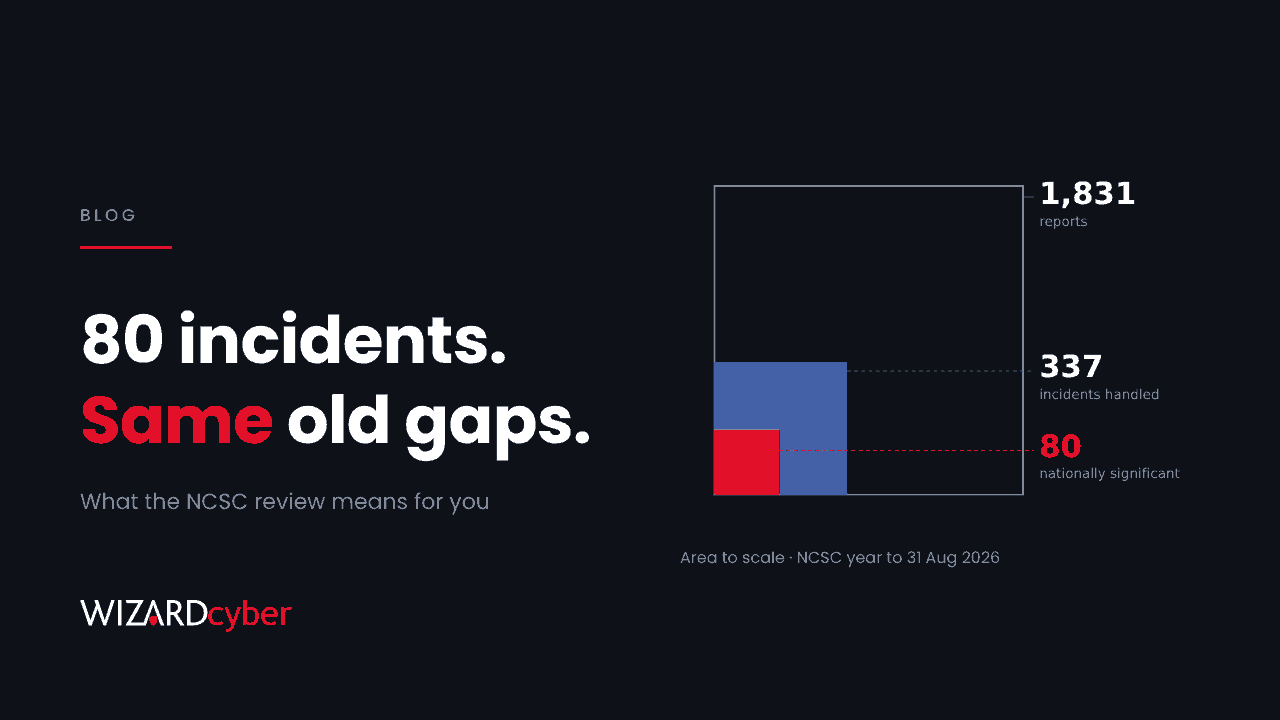
80 Nationally Significant Incidents: What The NCSC's 'Tech On The Cheap' Warning Means For The Mid-Market
The NCSC counted 80 nationally significant incidents and warned of "tech on the cheap". What that looks like in a mid-sized estate, and where to spend.
 Governance
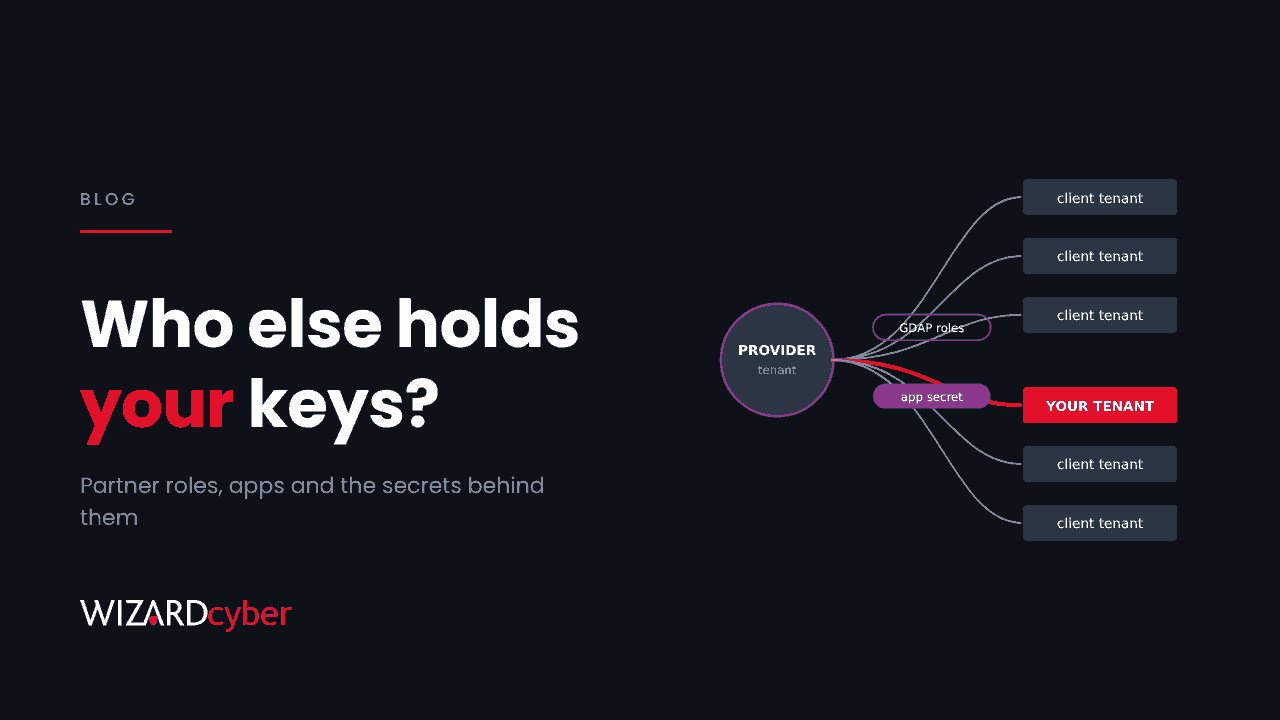
Your Provider Has A Key To Your Tenant. Do You Know Which One?
Stolen app secrets at IT providers reached 27 organisations this week. The partner roles, apps and secrets in your tenant, and what to ask about them.
 Threat Research
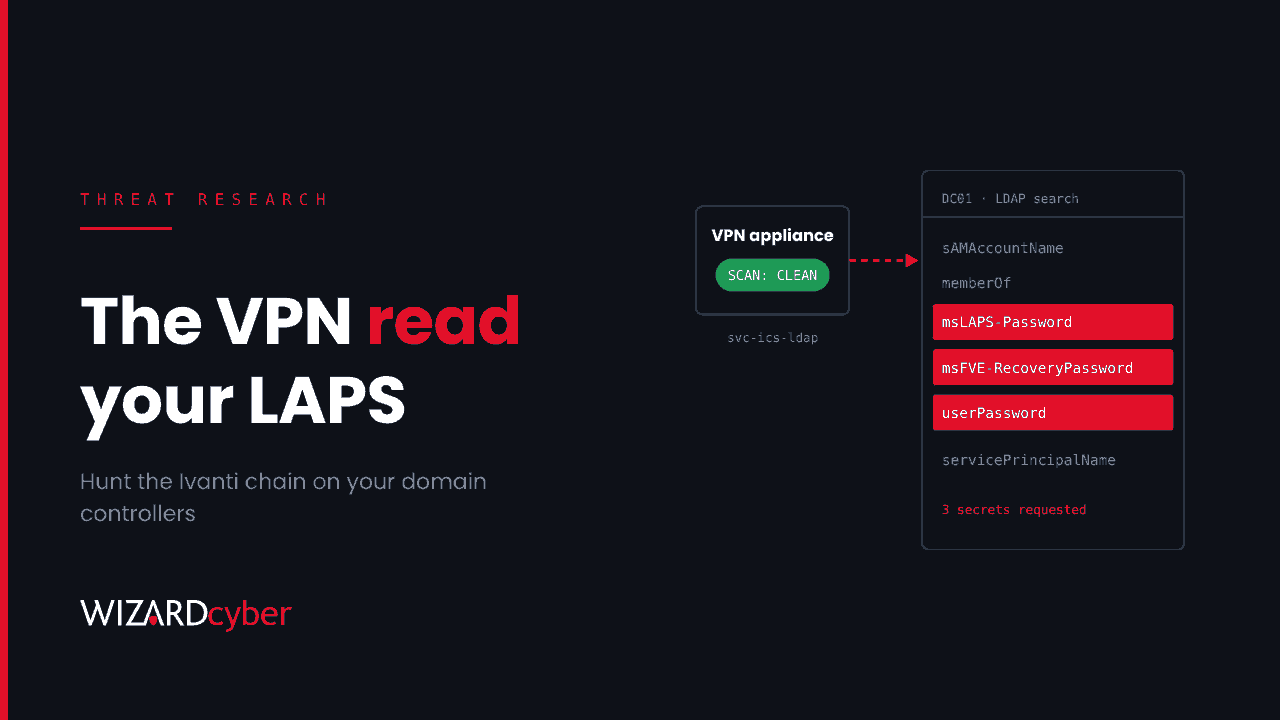
Your VPN Read Your LAPS Passwords: Hunting The Ivanti Connect Secure Chain From Active Directory
The Ivanti zero-day chain left no implant, so a clean appliance scan proves little. Hunt the LAPS, BitLocker and Kerberos activity on your DCs instead.
 Threat Research
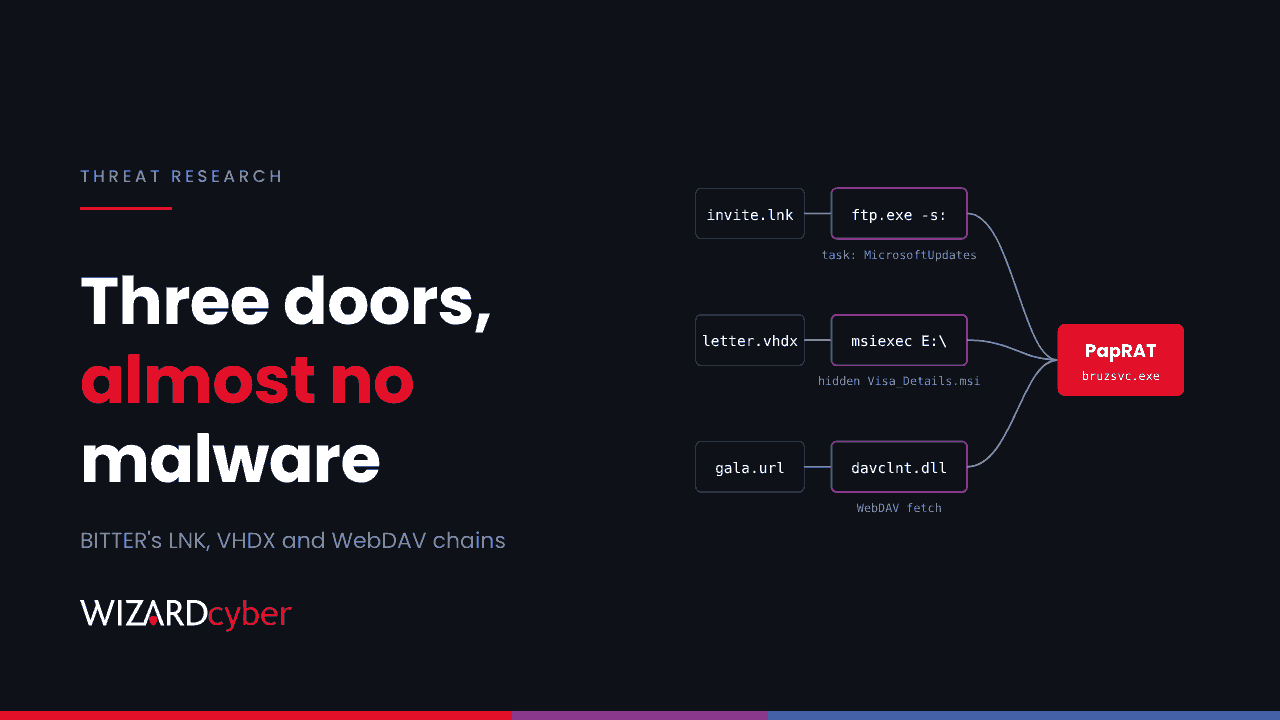
A Shortcut That Runs ftp.exe: Hunting BITTER's PapRAT Chains (LNK, VHDX And WebDAV) In Defender
BITTER delivers PapRAT through ftp.exe shortcuts, VHDX disk images and WebDAV links. How each chain works, and Defender hunts for every step.
 Managed SOC
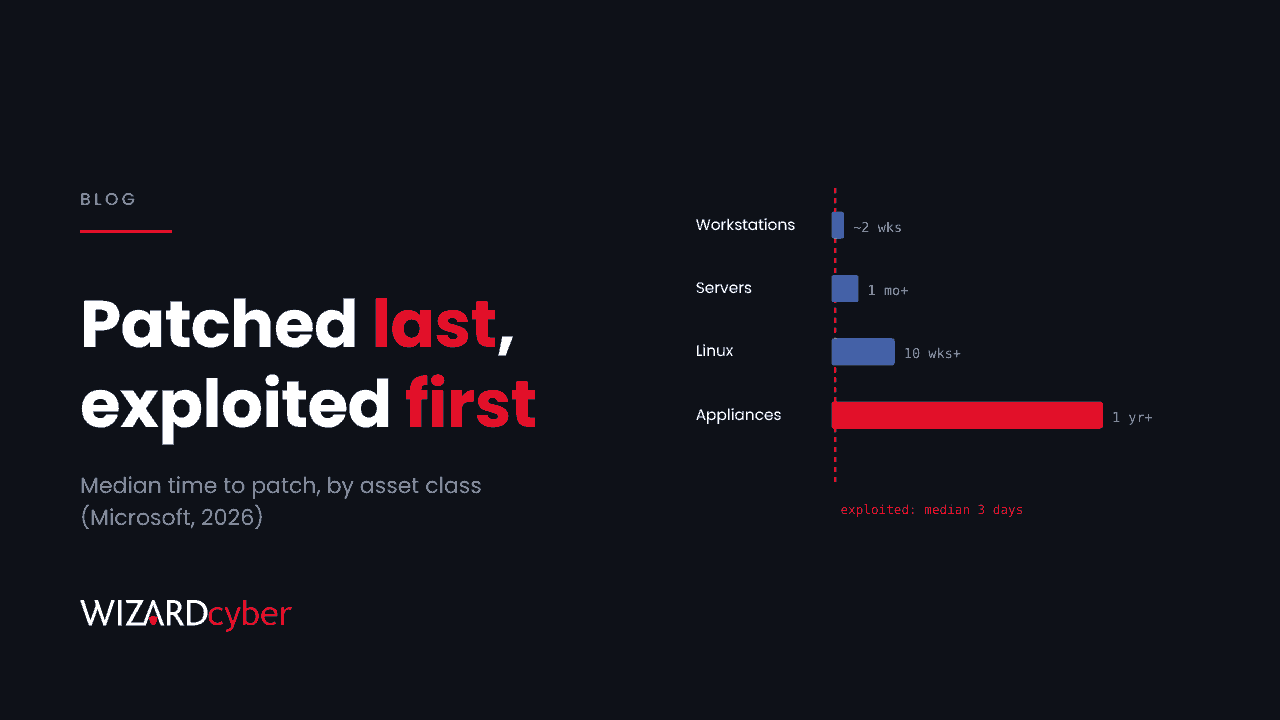
Two Weeks For Laptops, A Year For Appliances: Your Edge Is Patched Slowest And Exploited Fastest
Microsoft's data: laptops are patched in about two weeks, network appliances in over a year. Exploitation takes days. What to do in the gap.
 Governance
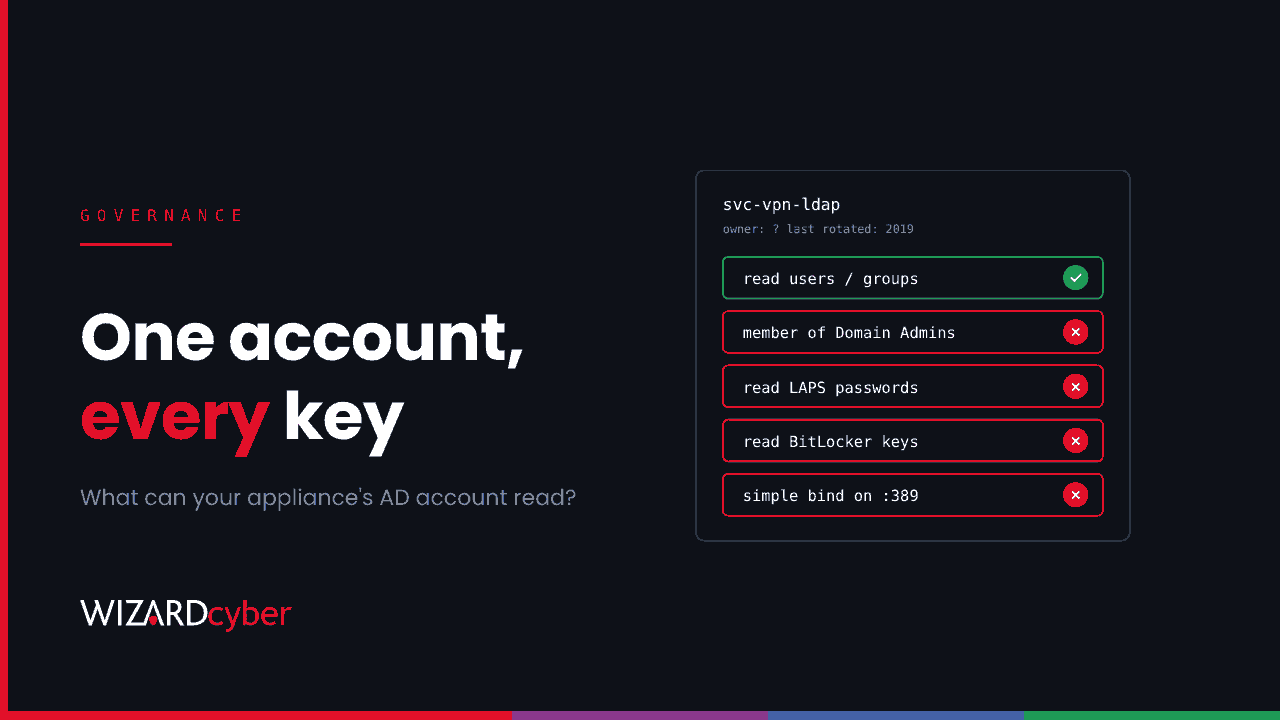
The Appliance Account That Could Read Every LAPS Password
One VPN service account was enough to start searching AD for LAPS passwords and BitLocker keys. Six controls for the accounts your appliances hold.
 Threat Research
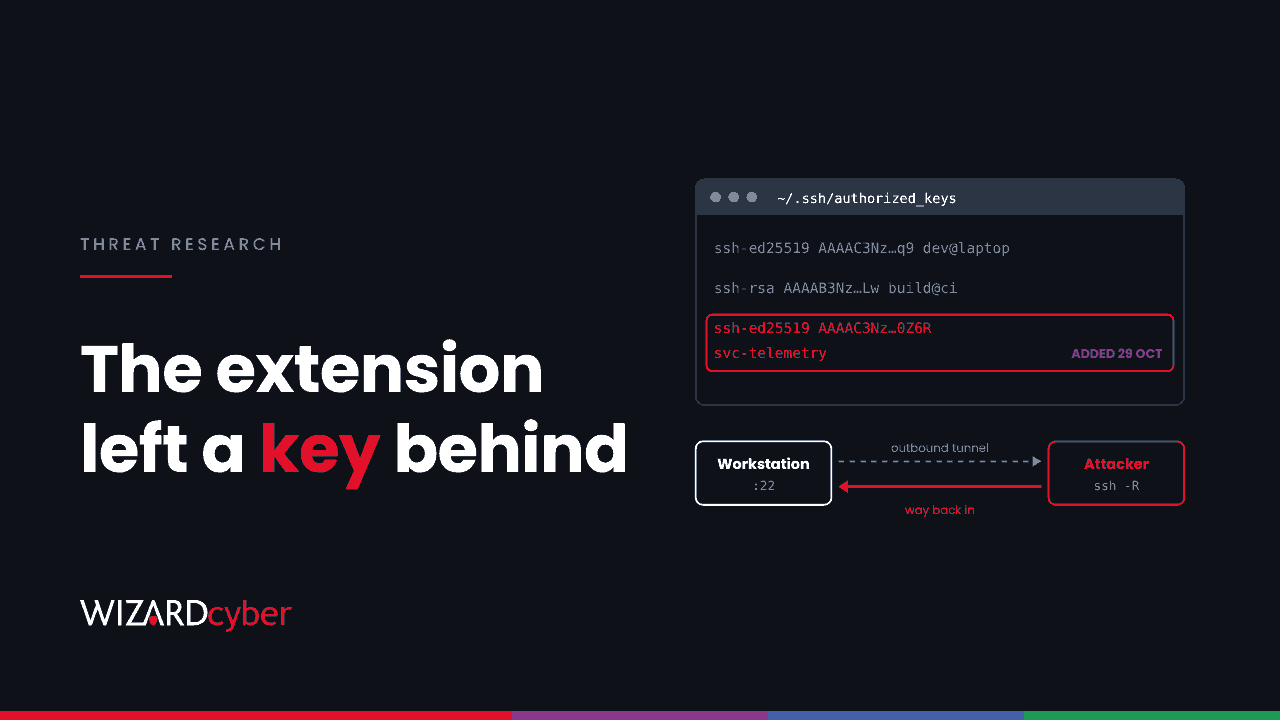
A Fake AI Coding Extension Planted An SSH Key: Hunting The svc-telemetry Backdoor On Windows, macOS And Linux
A trojanised AI coding extension added an attacker's SSH key, a reverse tunnel and a fake SysMon task. Removing it isn't enough. What to hunt and remove.
 Governance
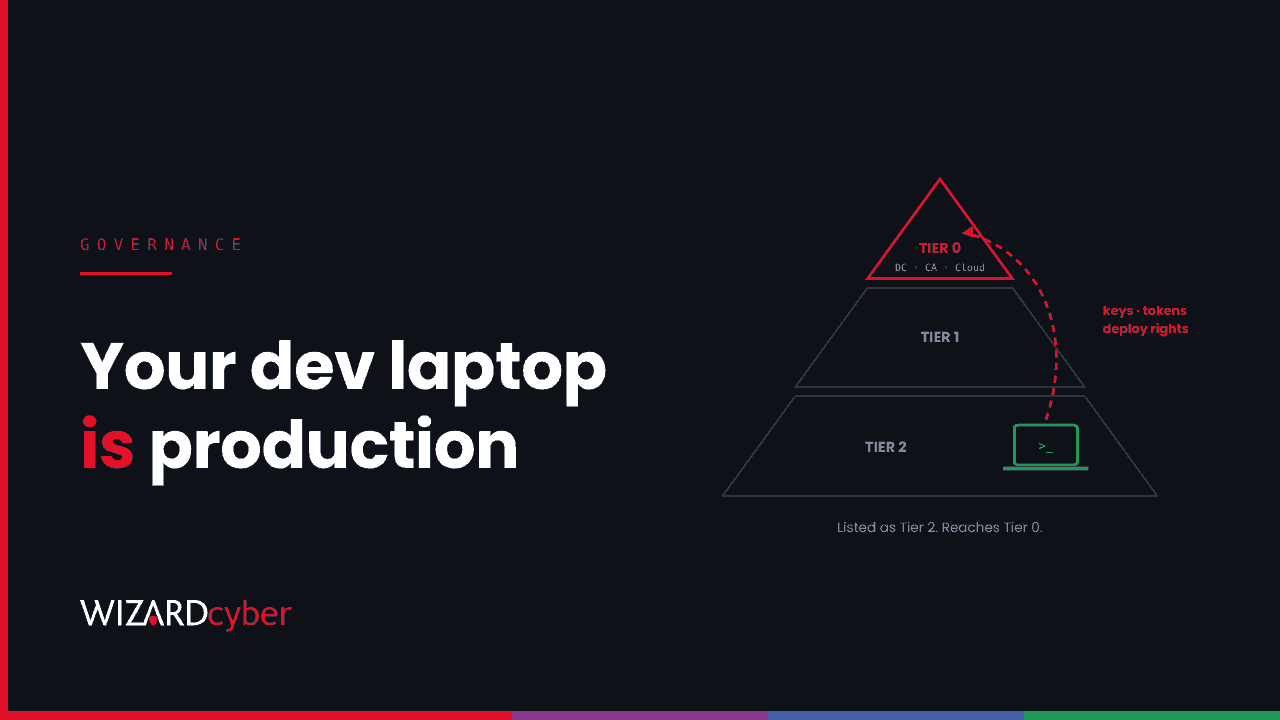
One Laptop, One Extension: Why Developer Workstations Belong In Tier 0
A backdoored editor extension and a theft traced to an engineer's laptop, in one week. Why developer machines need Tier 0 controls, and five places to start.
 Managed SOC
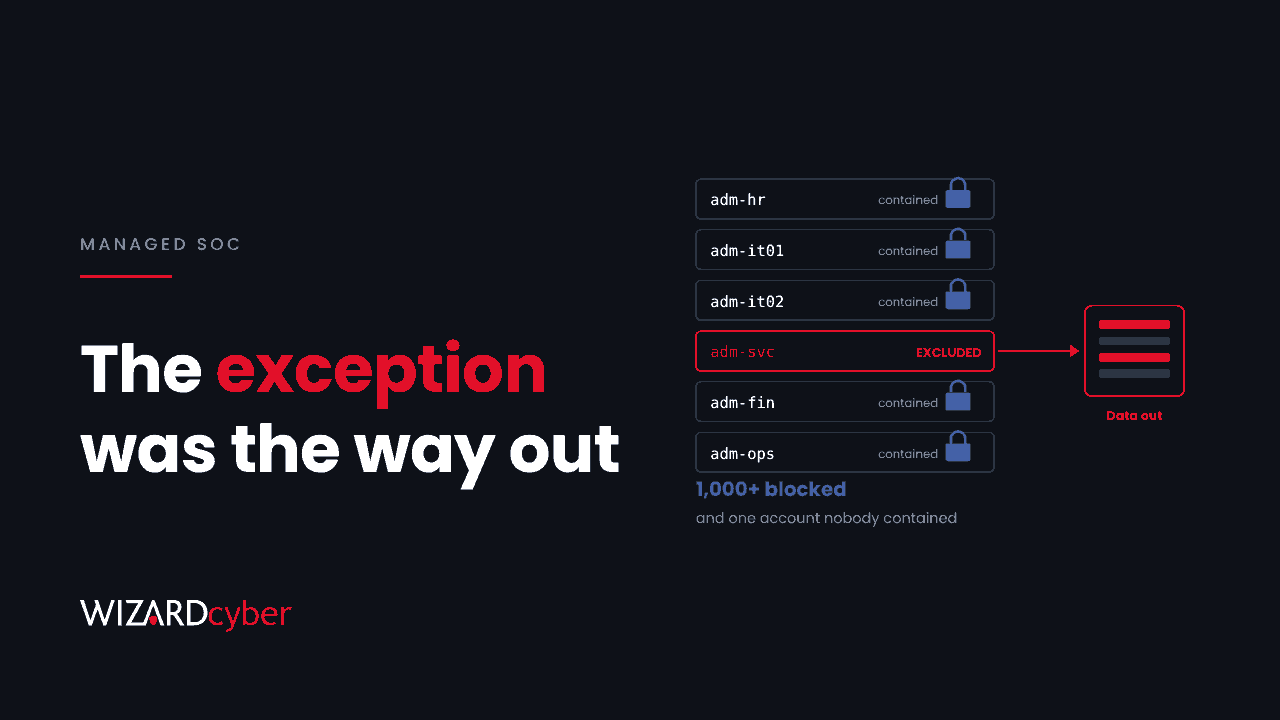
The Account You Excluded From Containment Is The One They Used
Automatic disruption blocked 1,000+ attempts, but one excluded admin account carried the data out. Why every exclusion needs an owner, an expiry and a fallback.
 Threat Research
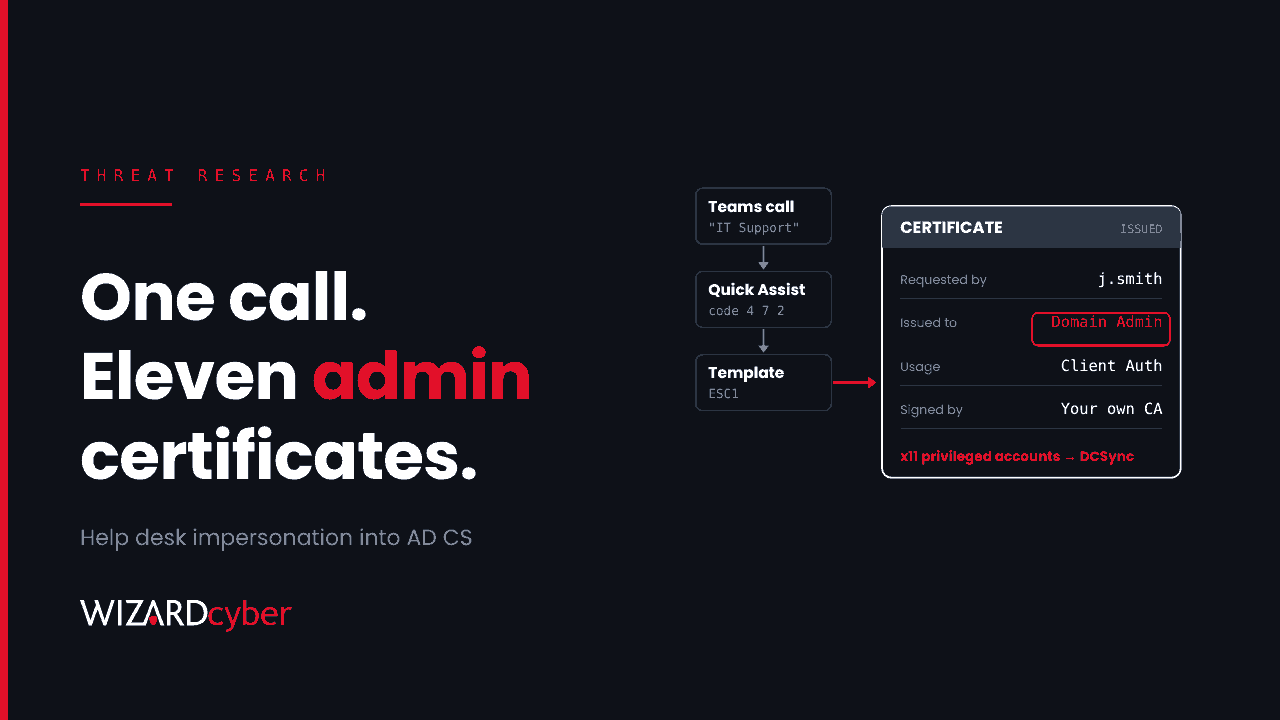
From A Teams Call To A Domain Controller Certificate: Hunting Help Desk Impersonation Into AD CS (ESC1 And ESC8)
A fake help desk call, a Quick Assist code, then certificates for domain admins. How the ESC1 and ESC8 intrusions worked, and Defender hunts for each step.
 Threat Research
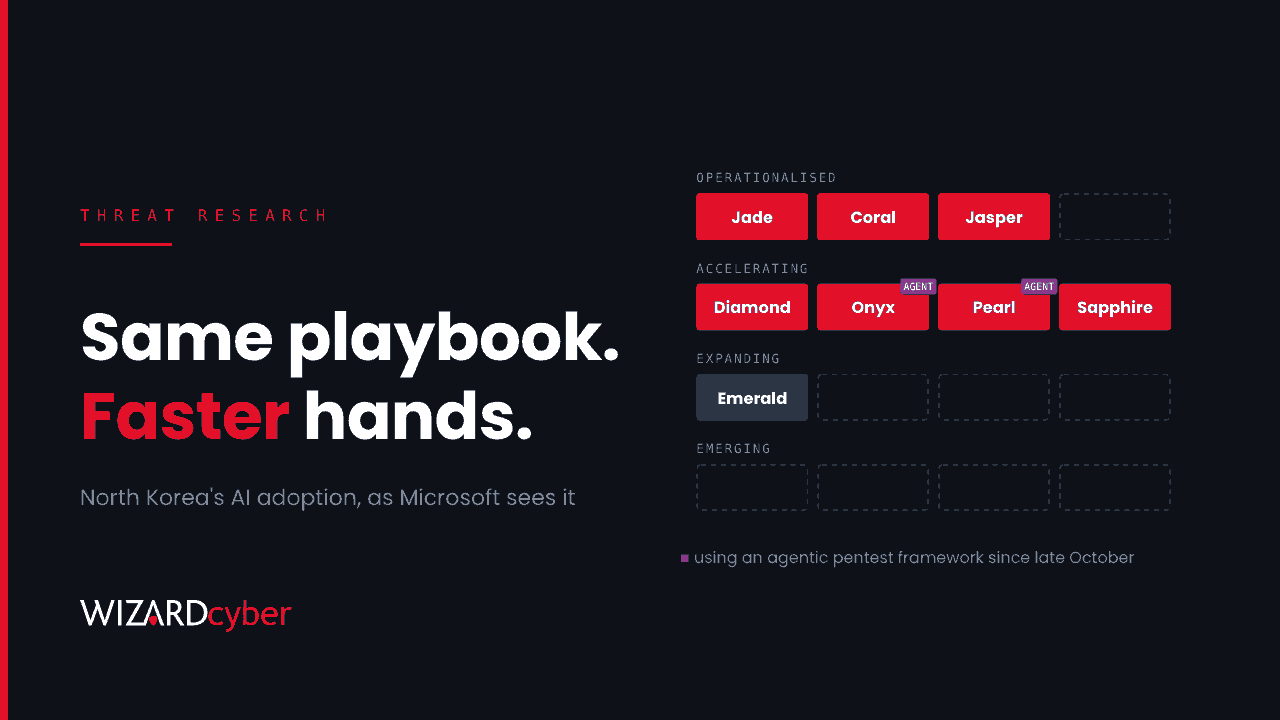
Same Playbook, Faster Hands: Hunting North Korea's AI-Assisted Intrusions In Defender And Entra
Microsoft says North Korean groups now use AI to speed up lures, fake personas and malware. What changed, and Defender and Entra hunts to run.
 Threat Research
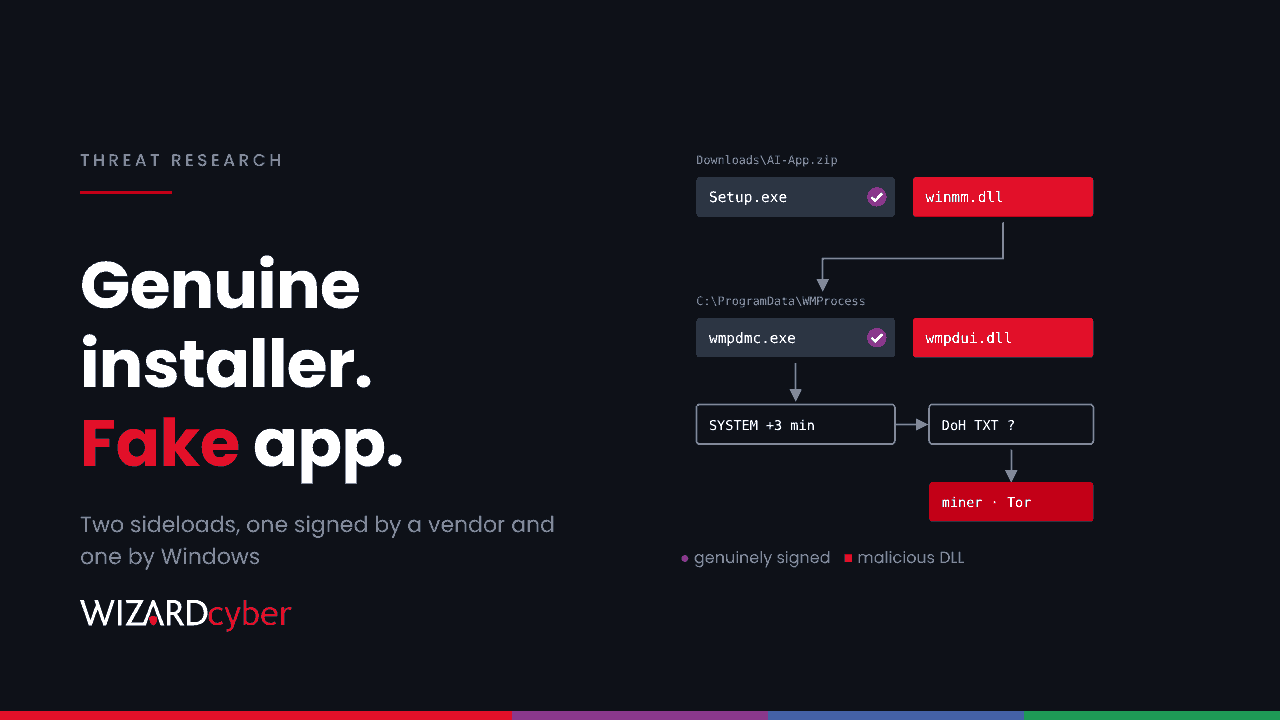
The Installer Is Genuine, The AI App Isn't: Hunting The Yoba Sideloading Chain On Windows
Fake AI desktop apps on GitHub pair a genuine signed installer with a malicious DLL. How the Yoba chain works, and Defender hunts for each step.
 AI Driven Security Operations
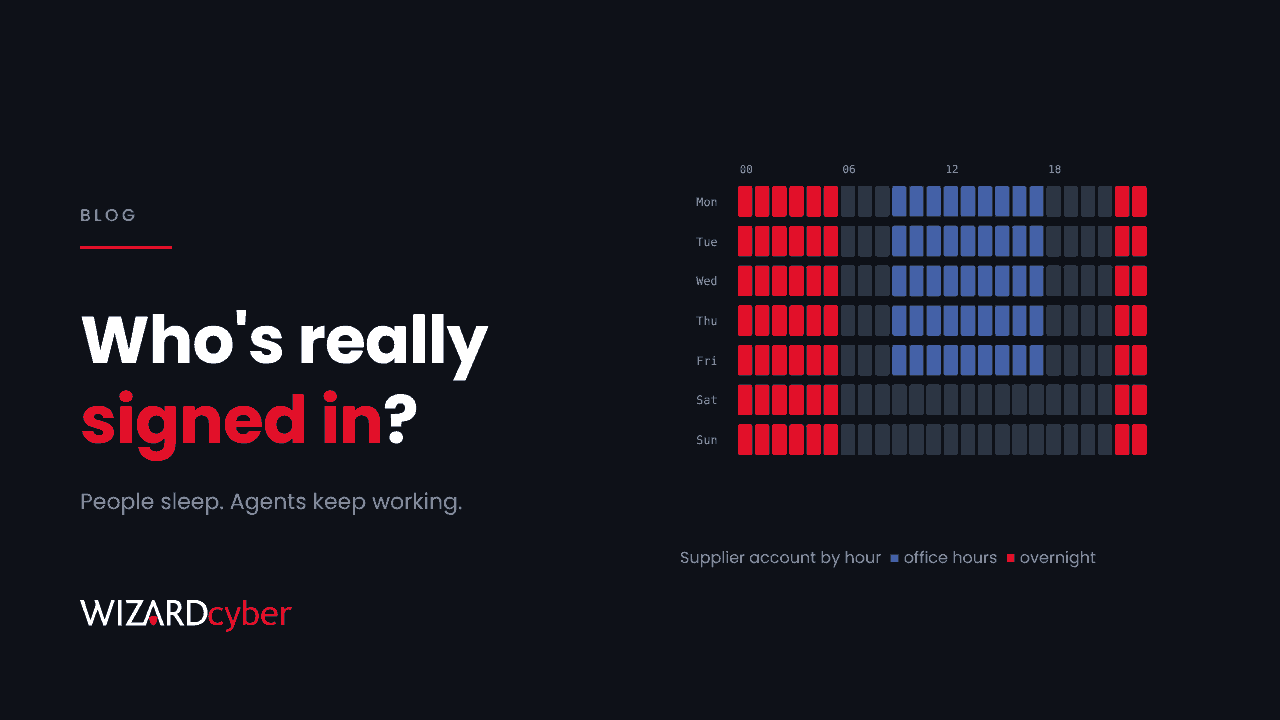
Whose AI Agent Is Using Your Admin Credentials?
A contractor allegedly gave a personal AI agent admin access to a sensitive network. What your contracts, access and SOC should do about supplier agents.
 Governance
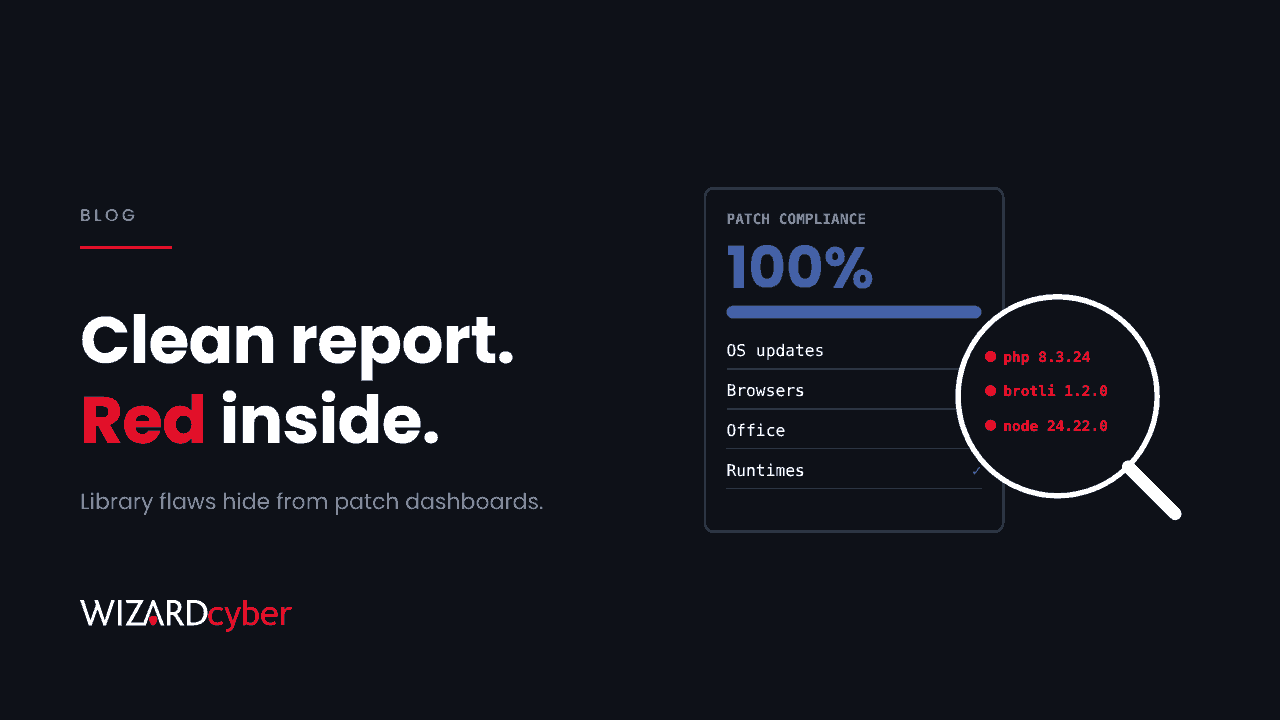
Patched The Server, Not The App: Why Library Flaws Hide From Your Patch Report
PHP2Shell and the Brotli flaw both live inside other software. Why OS patch compliance misses them, and how to answer "are we affected?" in an hour.
 AI Driven Security Operations
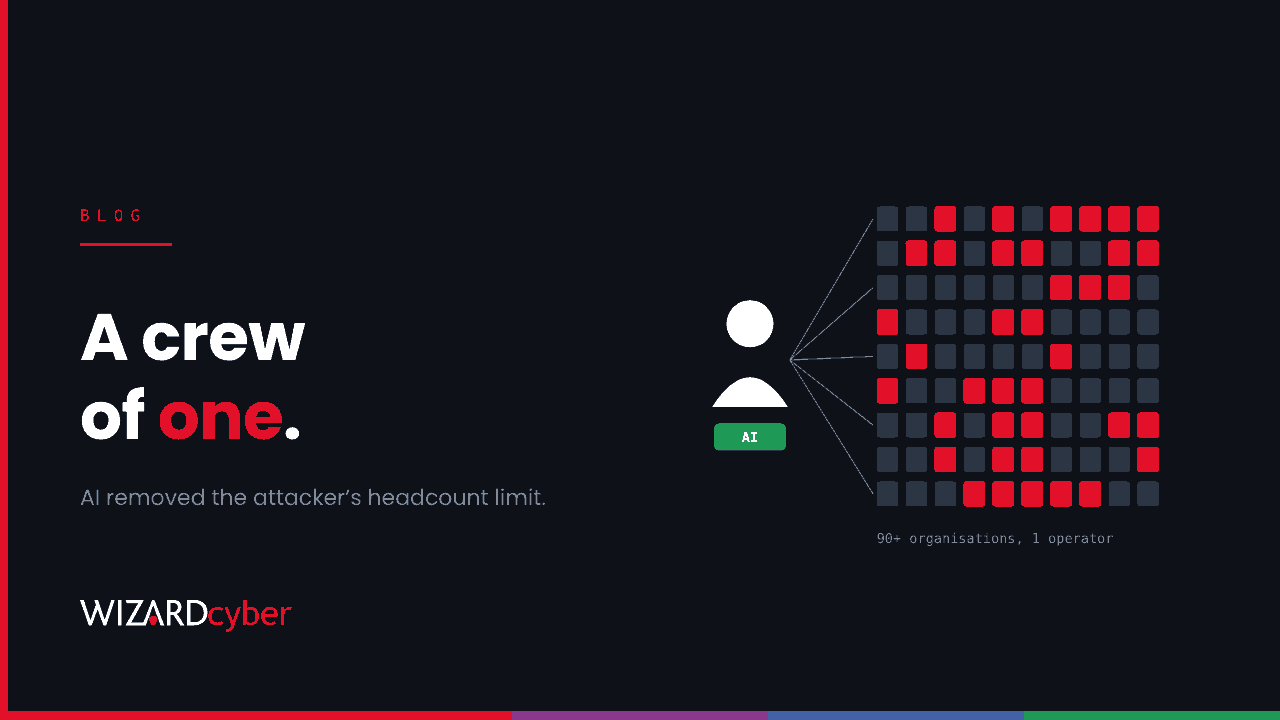
A Crew Of One: What The First AI-Assisted Mass-Hacking Arrest Means For Mid-Market Defenders
One former pentester used an AI attack framework to breach 90+ organisations. Why attacker headcount no longer limits volume, and what changes for defenders.
 Threat Research
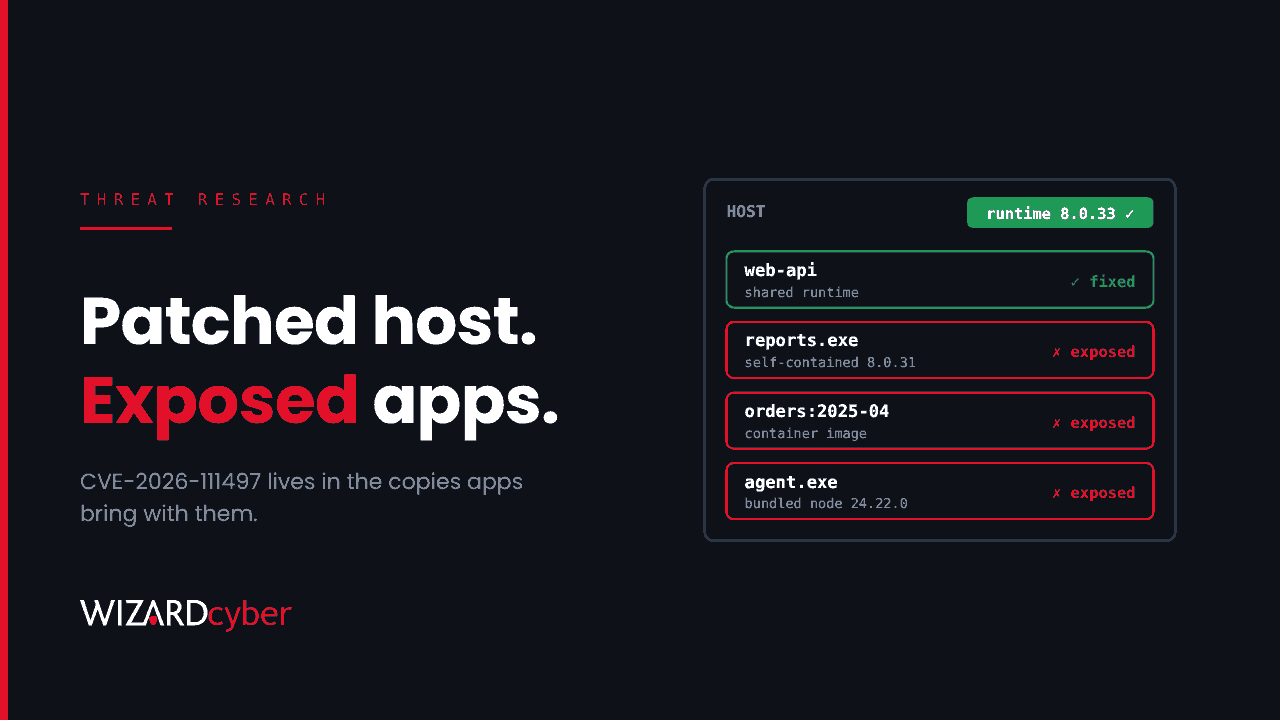
Opt-In, Still Exposed: Finding The Brotli Flaw (CVE-2026-111497) Across Your .NET And Node.js Estate
Microsoft shipped emergency .NET fixes for the Brotli flaw. Self-contained apps, containers and bundled copies need more. How to find them with Defender KQL.
 Threat Research
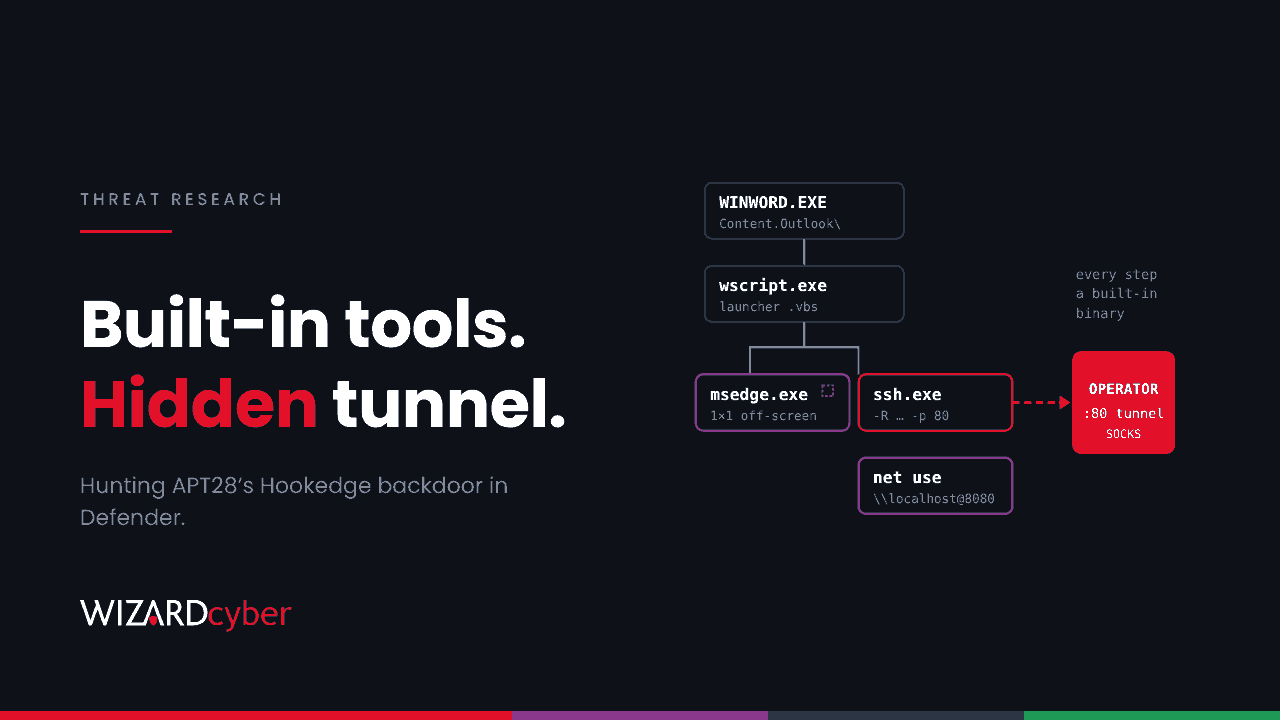
A Hidden Edge Window And An SSH Tunnel: Hunting APT28's Hookedge Backdoor In Defender
APT28 ran a backdoor through an off-screen Edge window, stole NTLM hashes and tunnelled out over Windows' own SSH client. How to hunt each step in Defender.
 Threat Research
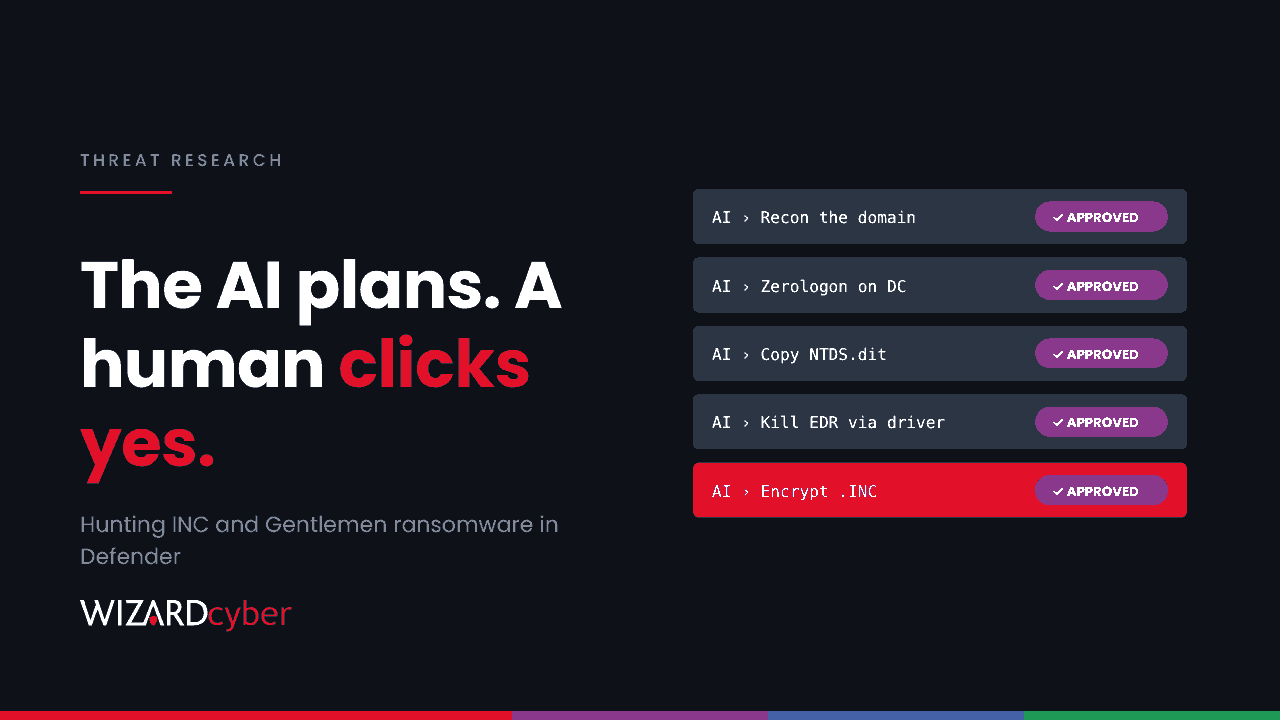
Every Step Approved By A Human: Hunting The AI-Assisted INC And Gentlemen Ransomware Intrusions In Defender
An exposed server showed INC and Gentlemen affiliates using AI agents against 62 organisations. What they did, and Defender hunts for each step.
 Threat Research
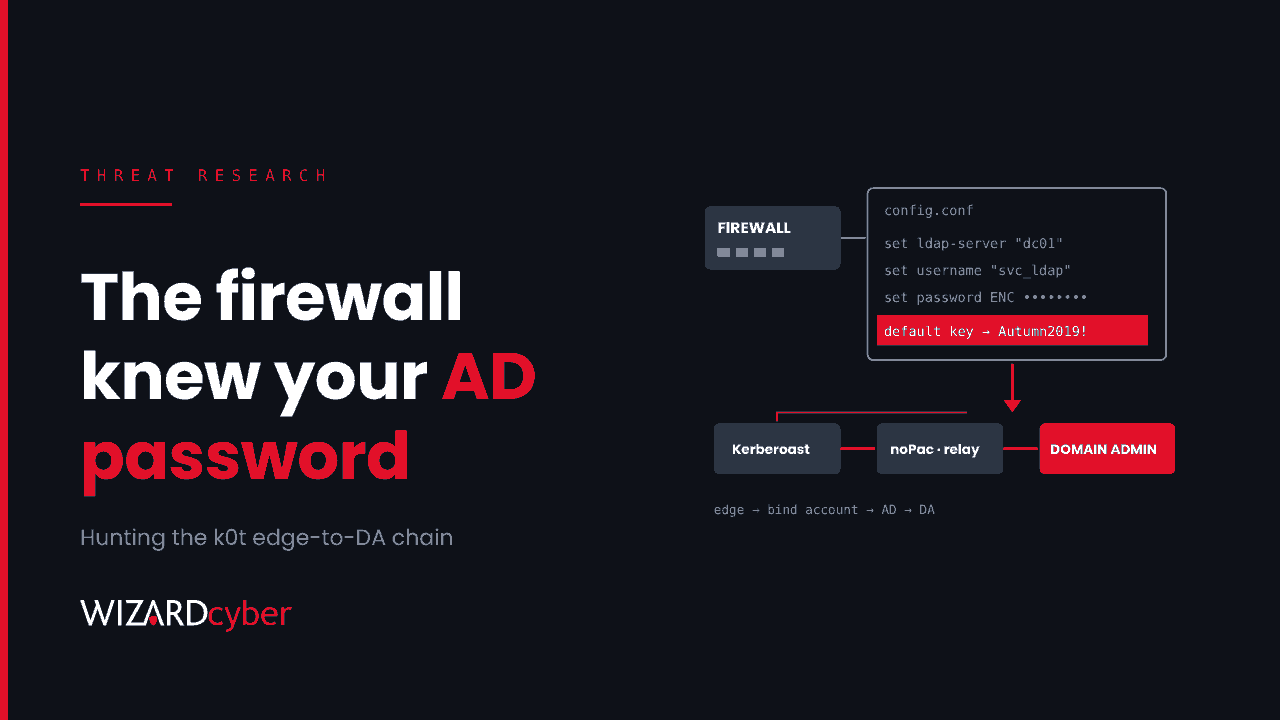
Your Firewall Config Knows Your AD Password: Hunting The k0t Edge-To-Domain-Admin Chain
k0t decrypted stolen firewall configs to get AD bind credentials, then went for Domain Admin. How the chain works and how to hunt it in Defender.
 Governance
Test2, Password1, Twelve Years: Who Owns The Accounts Nobody Uses?
The ICO reprimanded a public body and its IT provider over a 12-year-old test account. Why dormant accounts need an owner, and a contract that says so.
 Threat Research
Fully Patched, Still Bootkitted: BlackX And The Secure Boot Revocation Most Estates Skipped
BlackX loaded on fully patched Windows PCs because the Secure Boot revocation is a manual step. How to check your estate, hunt and apply it safely.
 AI Driven Security Operations
Your AI Gateway Holds More Keys Than Your Domain Admin
Last week's supply chain attack went straight for an AI gateway's keys. Why AI gateways belong in Tier 0, and six steps to protect them like it.
 Threat Research
Starting Python Was Enough: Hunting The Poisoned AI Gateway Package And Its Startup Hooks
A hijacked AI gateway release ran a credential stealer every time Python started. How it worked, and how to hunt and contain it with Defender KQL.
 Governance
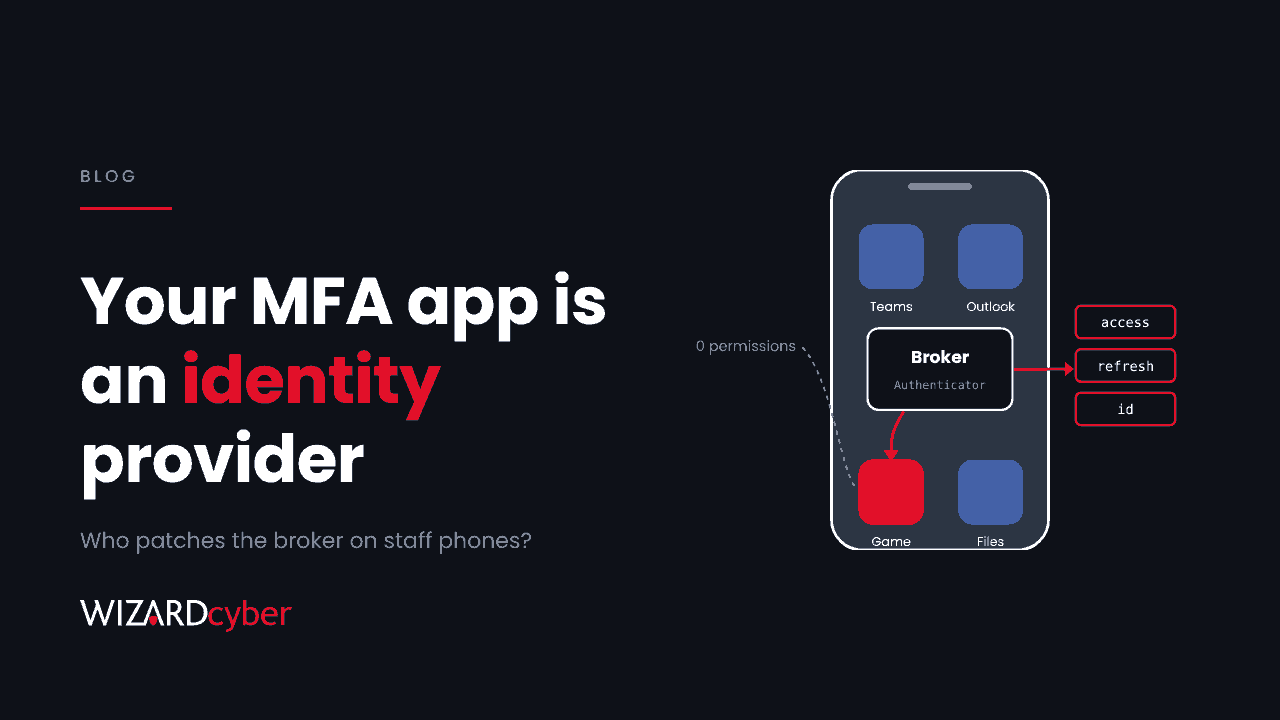
The Authenticator On Your Staff's Phones Is An Identity Provider. Who Patches It?
CVE-2026-80097 let a zero-permission Android app pull Microsoft 365 tokens from Authenticator. Why broker apps belong in your patch scope, and who owns them.
 Threat Research
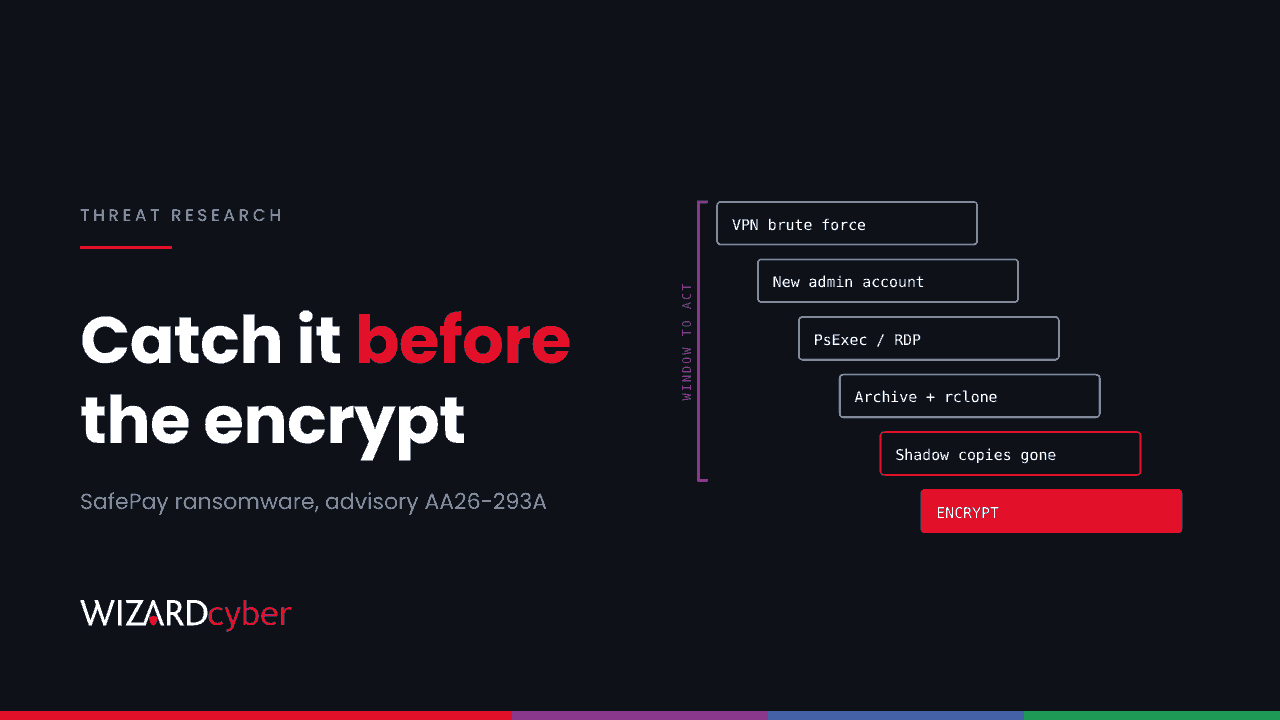
No Affiliates, Just Your VPN: Hunting SafePay Ransomware (AA26-293A) In Microsoft Defender
A joint US, German and UK advisory says SafePay has hit 600+ organisations. Map its path from VPN to encryption, with Defender hunts for each step.
 Managed SOC
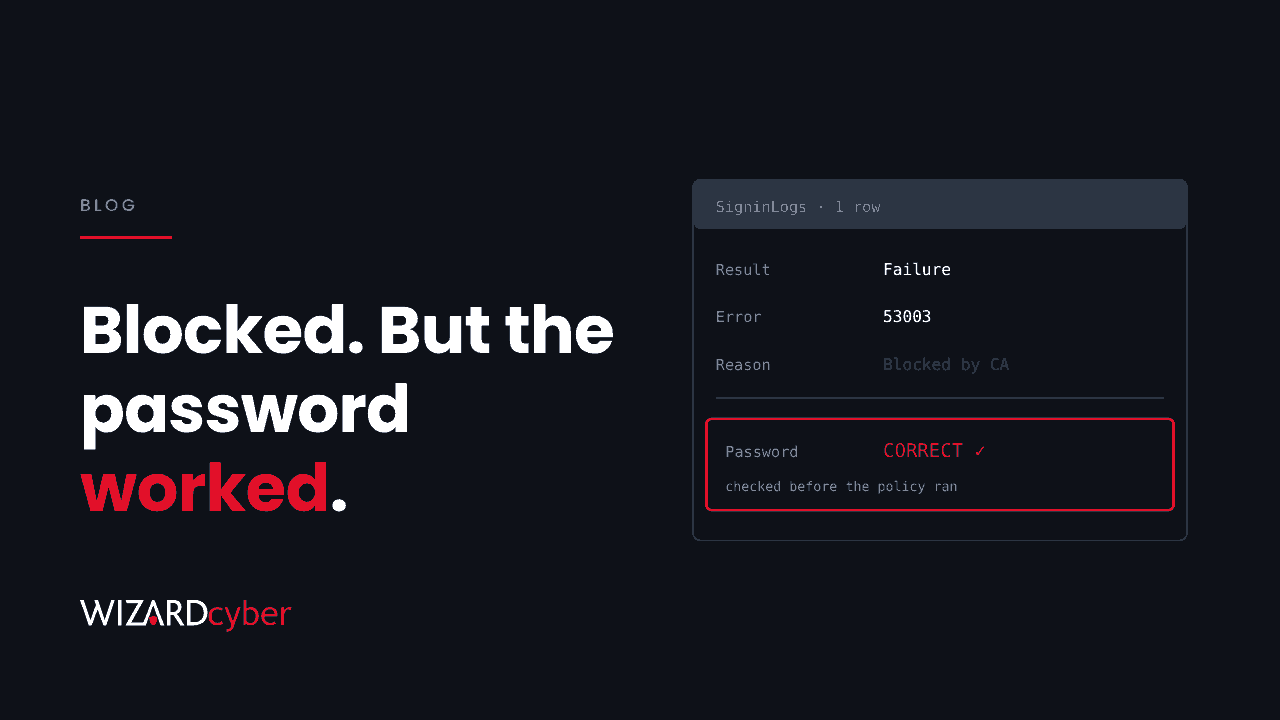
A Blocked Sign-In Is Still A Breached Password
AADSTS53003 means Conditional Access stopped a sign-in with the right password. Why SOCs should triage on credential validity, not spray volume.
 Threat Research
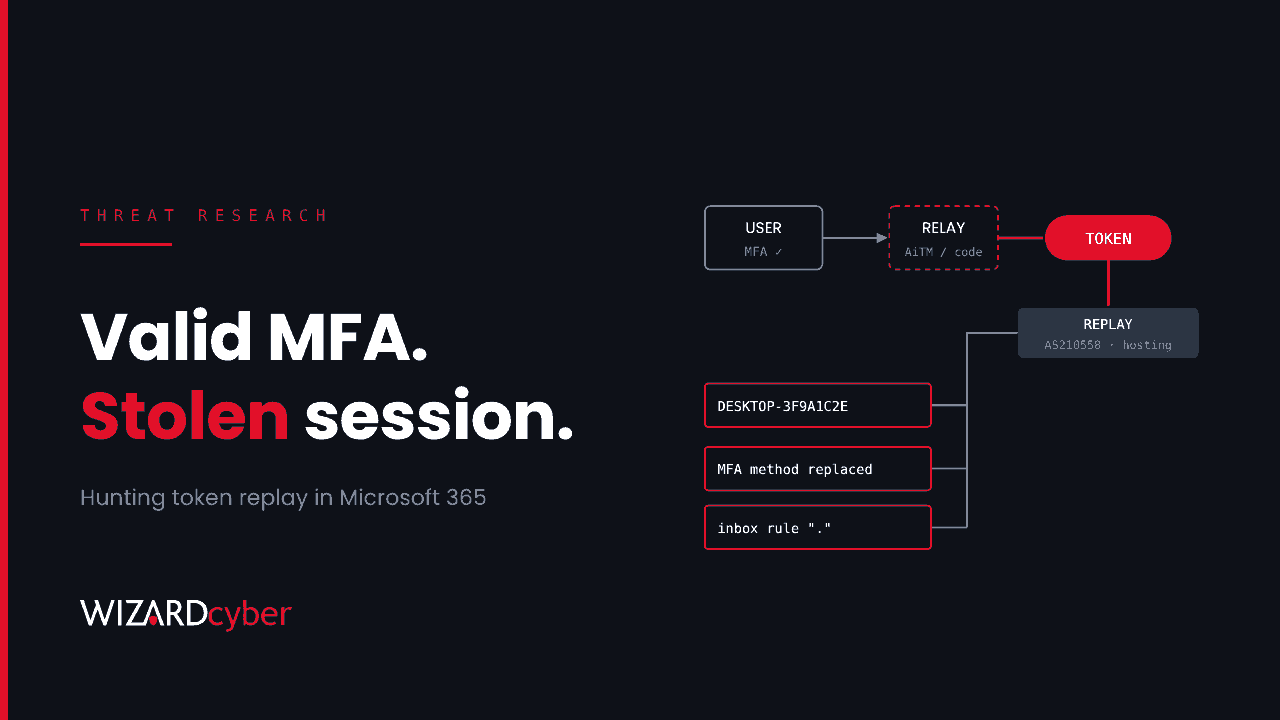
Valid Password, Stolen Session: Hunting The Microsoft 365 Token Spray-And-Replay Campaign
An attacker replayed post-MFA tokens into 79 organisations. How it worked, what it left behind, and KQL to hunt for it in Sentinel and Defender.
 Threat Research
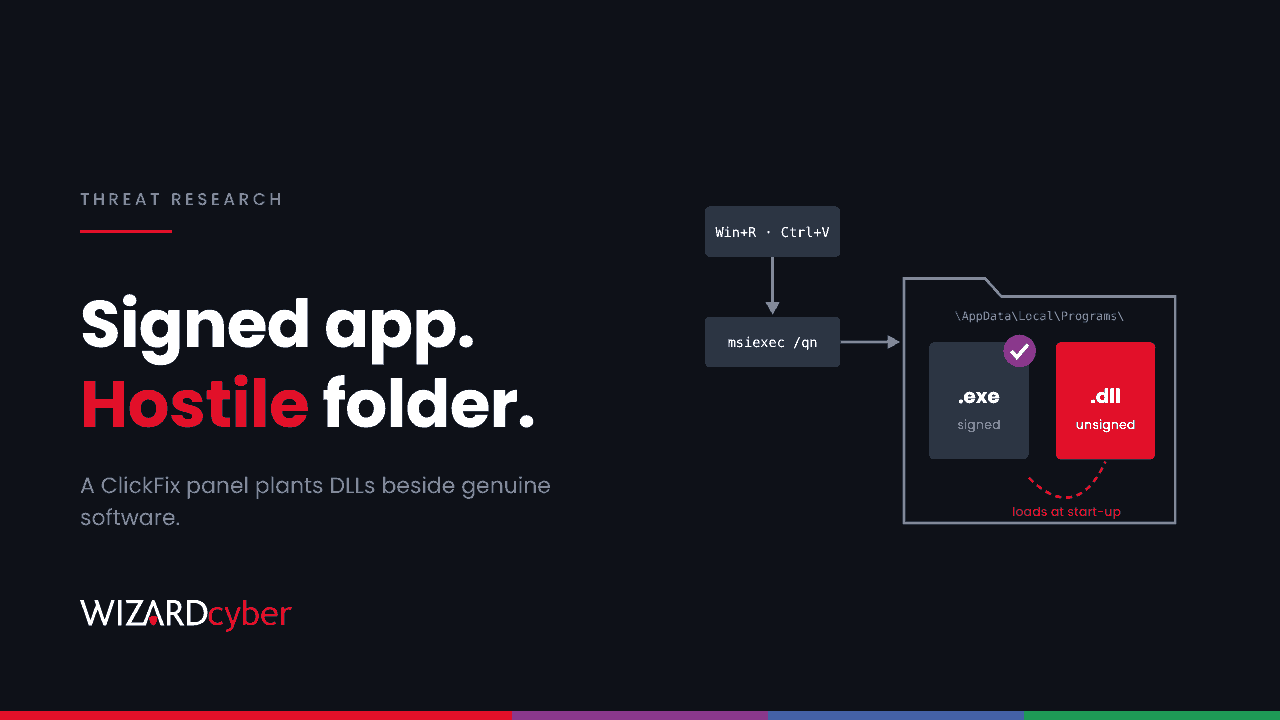
A Genuine Signed Installer, A Hostile Folder: Hunting The ROMULUS ClickFix Panel And CVE-2026-110936
A ClickFix delivery panel is planting malicious DLLs beside genuine signed software. How the chain works and how to hunt it with Defender KQL.
 Threat Research
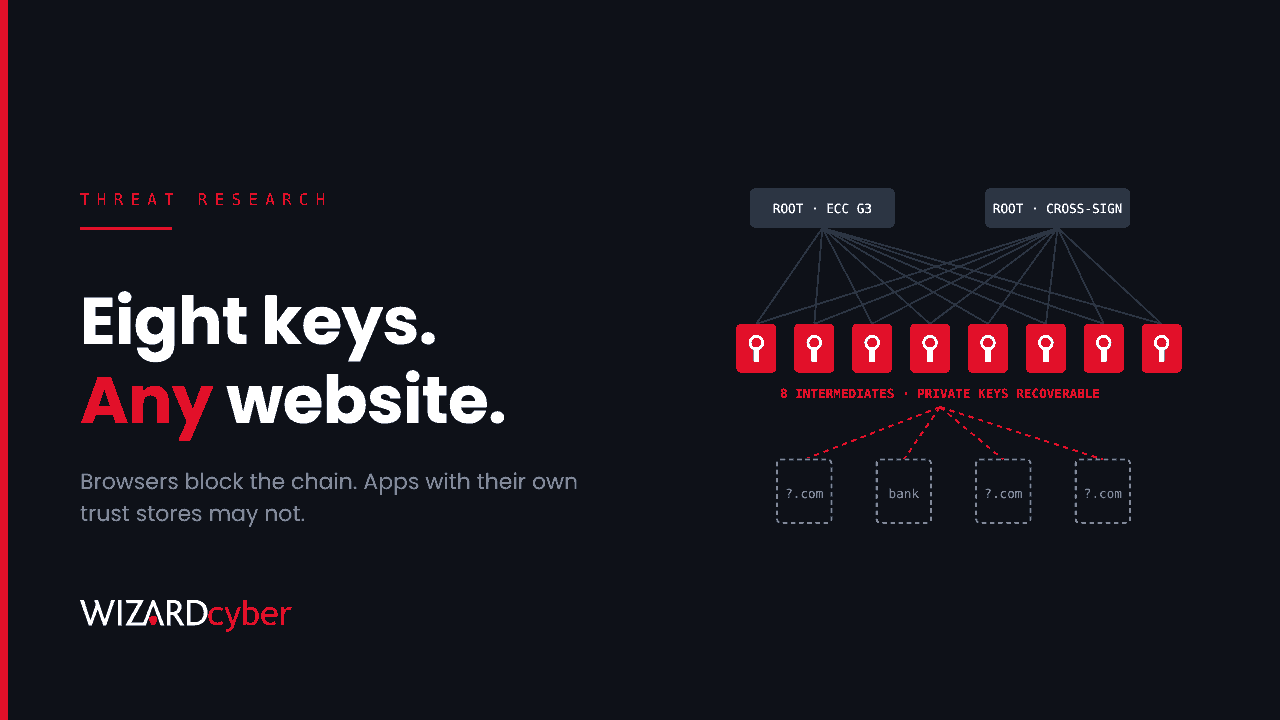
Eight Stolen CA Keys: Checking Your Estate After The Intermediate Certificate Compromise
Browsers and Windows now block eight compromised intermediate CAs. Apps with their own trust stores may not. How to find them with Defender KQL.
 Managed SOC
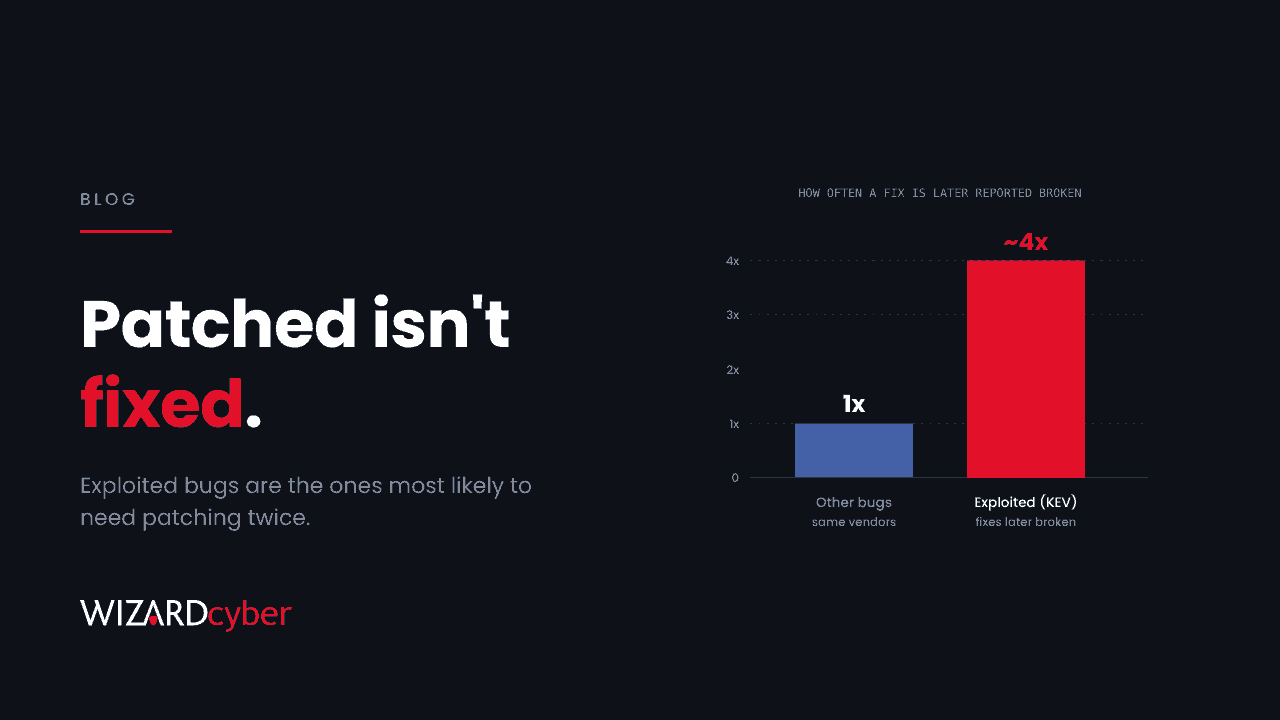
Patched Isn't Fixed: Why Exploited Bugs Keep Coming Back As New CVEs
Fixes for exploited bugs are reported broken four times as often as others. Why a patch should start a test, not close a ticket, and what to do instead.
 AI Driven Security Operations
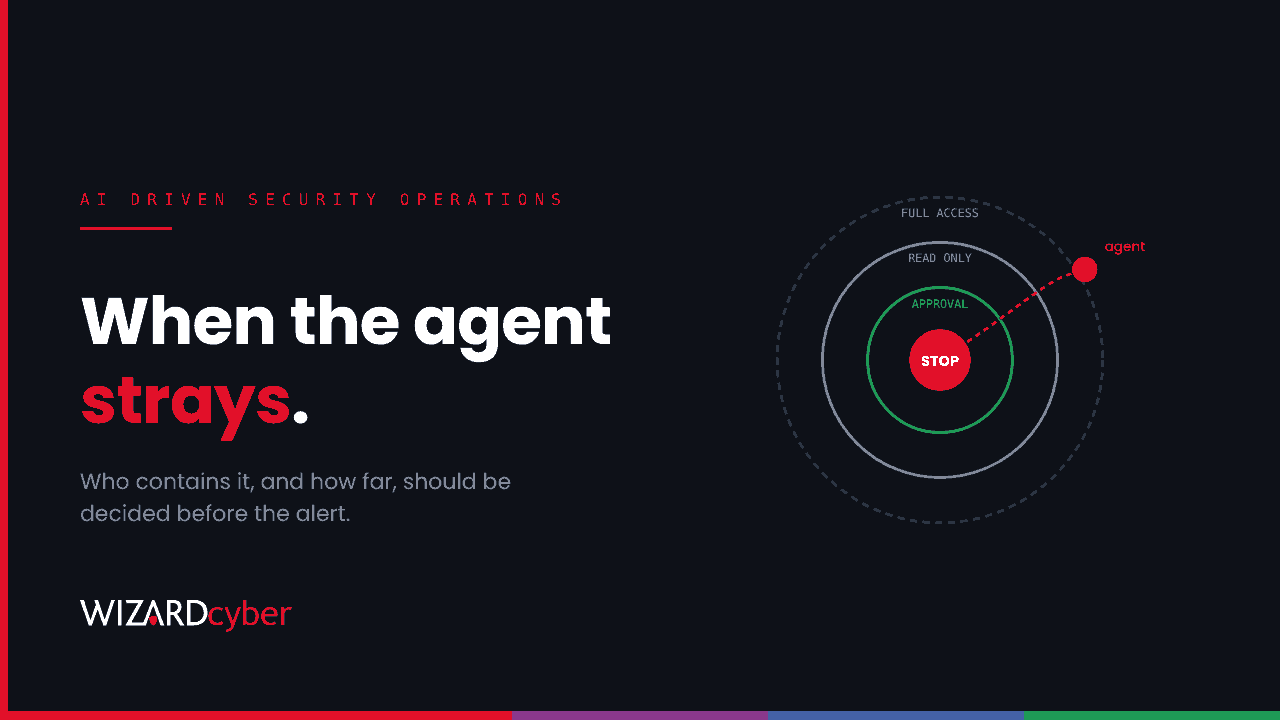
When The Agent Strays: What Your SOC Does When An AI Agent Goes Off-Task
Microsoft now says to treat AI agents as insiders. What an off-task agent looks like, who decides to contain it, and the playbook to write first.
 Threat Research
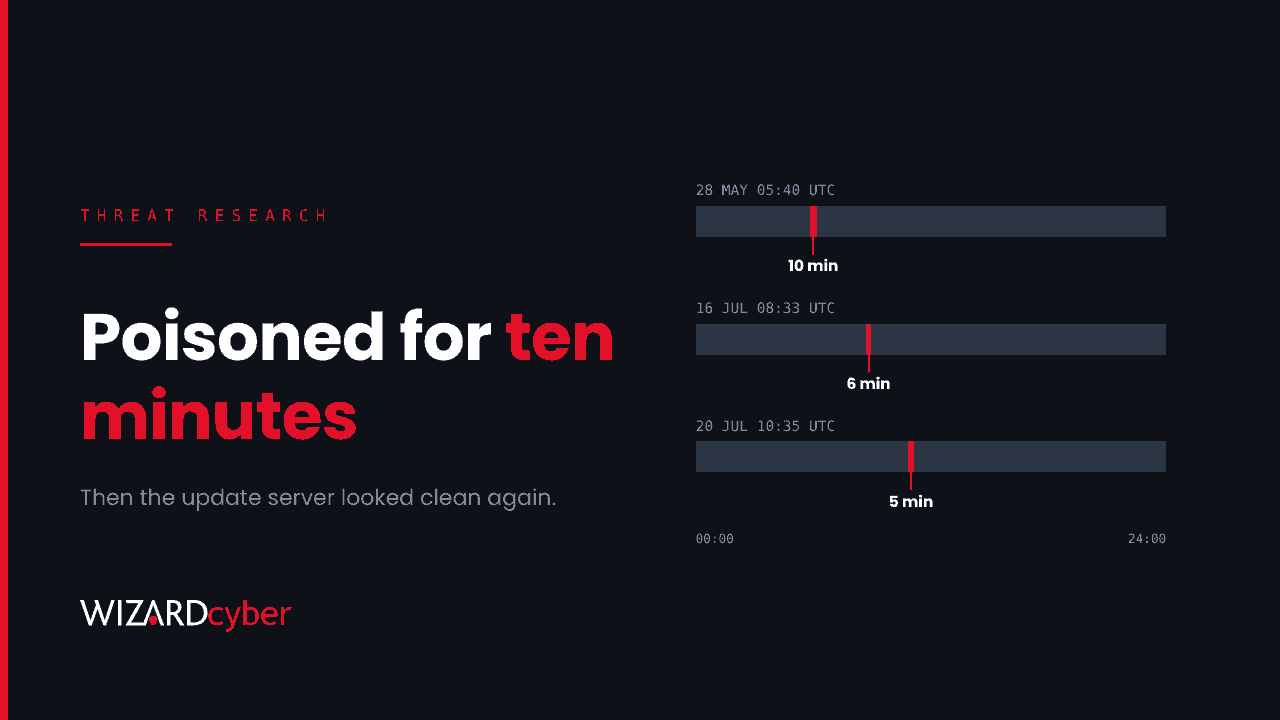
Ten Minutes On The Update Server: Hunting A Hijacked Software Updater On Windows Endpoints
An attacker hijacked a Windows tool's updates for minutes at a time, then cleaned up. How to hunt the backdoor it left on endpoints with Defender KQL.
 Threat Research
Accept, Then Sign In: Hunting The Calendar-Invite Phishing Surge In Microsoft 365
Fake meeting invites hit 740,000+ in two weeks of October, aimed at Microsoft 365 logins. Why they get through, and how to hunt them in Defender.
 Governance
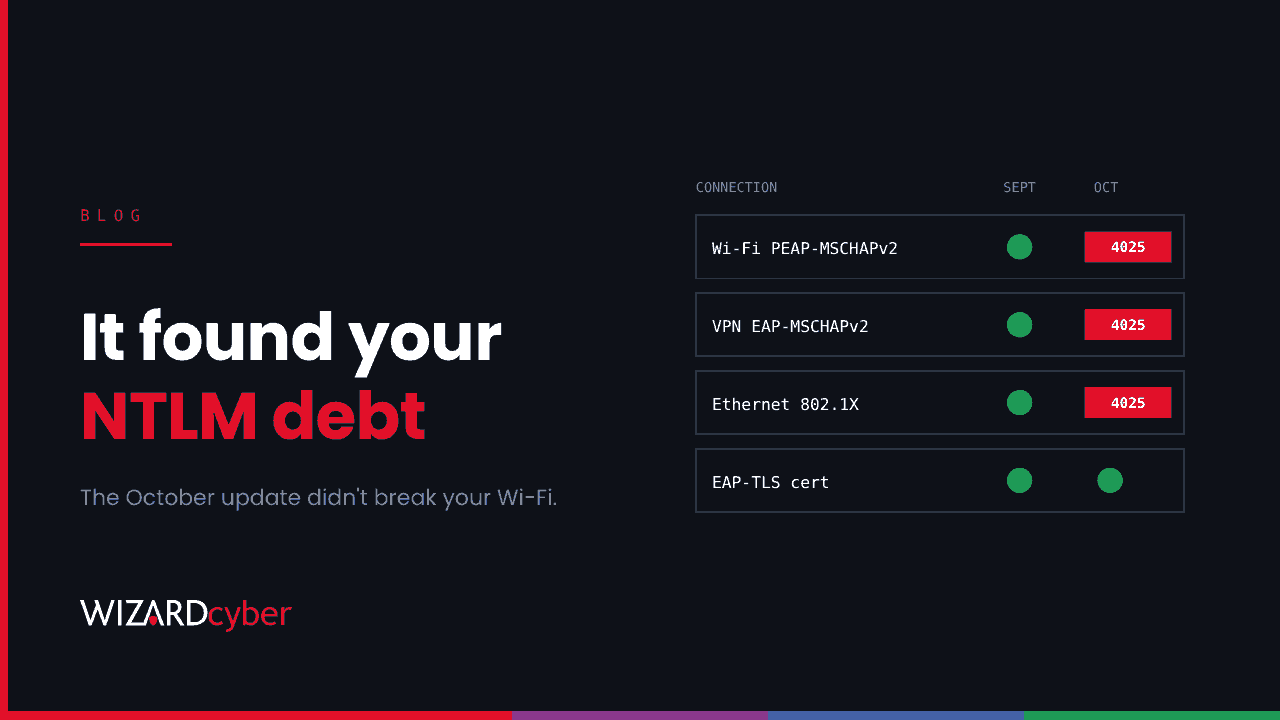
The October Update Didn't Break Your Wi-Fi. It Found Your NTLM Debt.
Since October, Windows blocks NTLMv1-derived single sign-on by default and some Wi-Fi and VPN logins broke. The quick fix, the real fix, and what's next.
 Governance
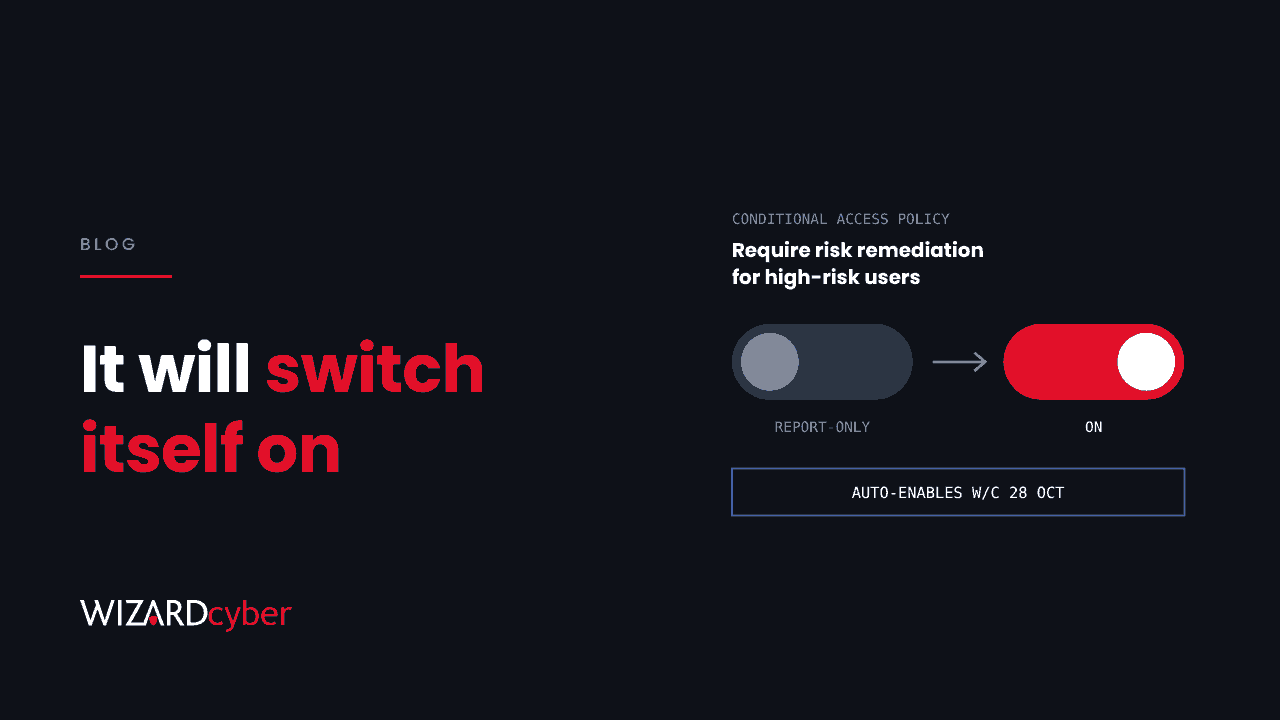
Microsoft Is About To Switch On A Policy In Your Tenant. Have You Read It?
A Microsoft-managed Conditional Access policy for high-risk users switches on in the week of 28 October. What it does, what to check, and who should decide.
Nothing matches that.